
The iceberg of web app exploits

Source link
Related Articles
All Mix →
High Risk Vulnerabilities within the DoD – Exploiting Coldfusion, Dotnet Nuke, Oracle, and more | by Alyssa Herrera
The Department of Defense Launched a bug bounty program on November 21st, 2016 on Hackerone. This allowed researchers to report vulnerabilities on any military domain,…
HackerOne’s Approach to Triage | HackerOne
Table of Contents Meet the Extension of your Security Team Triage is just the first step Getting Results The best programs on HackerOne have the…
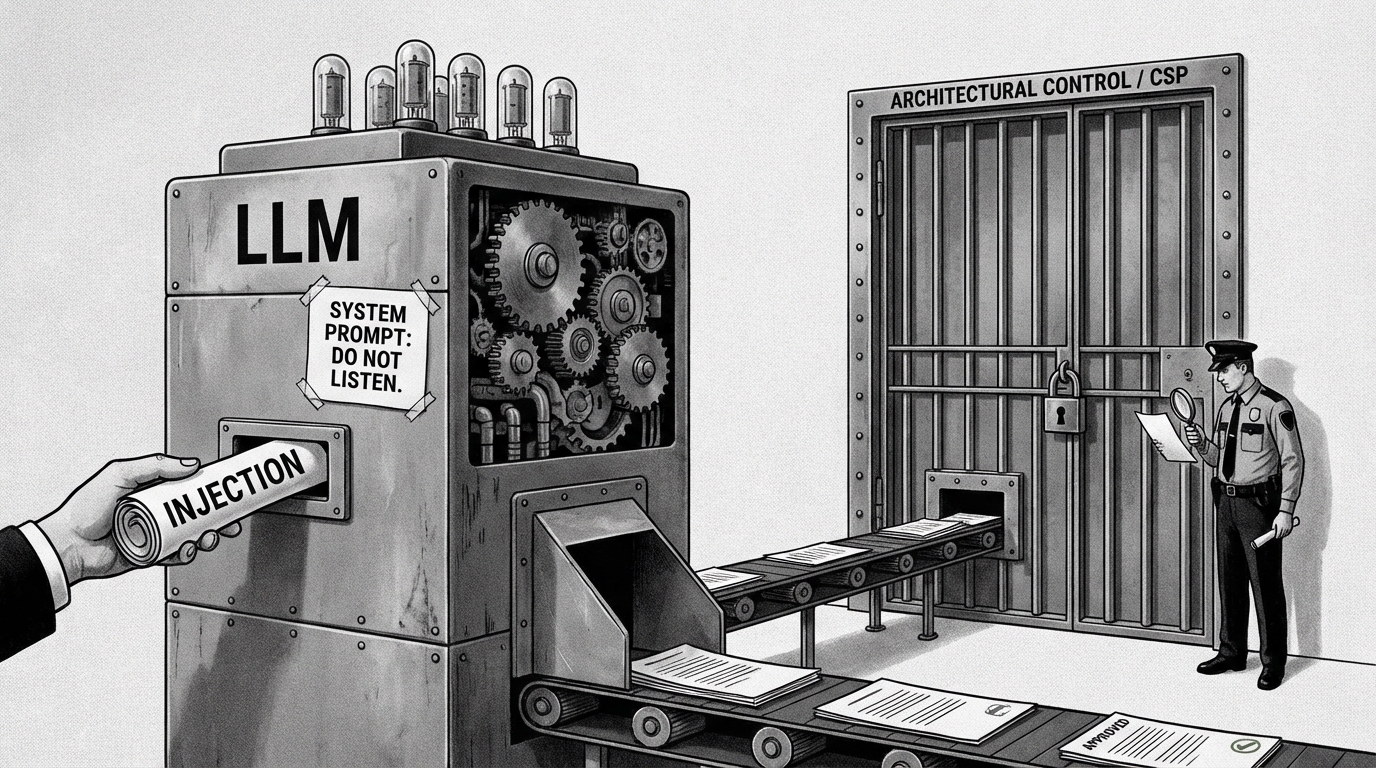
Prompt Injection Isn’t a Vulnerability · Joseph Thacker
Table of Contents The Real Bug is the Resulting Action Bug 1: Data Exfiltration via Dynamic Image Rendering Notes for AI Notes for AI Notes…
Home for One Year | Daniel Miessler
Sometime around this week marks one year that I’ve been back home in the Bay Area. It’s been the best year of my life. My…
Visma’s Ioana Piroska on Securing the Development Lifecycle Through Bug Bounties
Visma is a leading business solution provider in Northern Europe, focusing on business optimization and management tools in a variety of industries. The company’s nearly…
Hidden XSS? No User Interaction!
@kinugawamasato가 정말 멋진 페이로드를 가지고 왔습니다. 최근 글 XSS Bypass: alert_?_(45)에서 이야기 드렸듯이 요즘 XSS 벡터에 대한 리서치가 활발해지고 있는데요, 드디어 Hidden XSS에서 사용자 인터렉션을…