
UMBC Cyberdawgs CTF: The Hacker One

Source link
Related Articles
All Mix →
Exploiting JWT vulnerabilities to achieve RCE
At Intigriti, we host monthly web-based Capture The Flag (CTF) challenges as a way to engage with the security research community. This month, we’ve decided…
Personal Daemons and Wuffie | Daniel Miessler
Table of Contents The Personal Daemon Use Cases Wuffie Total Karma Ratings for Popular Locations Everyone knows the future of technology lies with the individual.…
Wallarm at OWASP Global AppSec DC 2023
Table of Contents Why OWASP 2023 Global AppSec Event? Meet Wallarm at the Event Why Choose Wallarm for API Security? Not Going to OWASP AppSec…

Announcing the Largest DoD Bug Bounty Challenge Ever: Hack the Air Force
The Air Force is asking hackers to take their best shot following the success of Hack the Pentagon and Hack the Army bug bounty challenges.…
Detectify Blog – Here’s how EASM fills gaps missed by AppSec solutions
Table of Contents Why does the AppSec tech stack fall short? Developer experience influences how quickly an organization can resolve vulnerabilities Security scoring systems don’t…
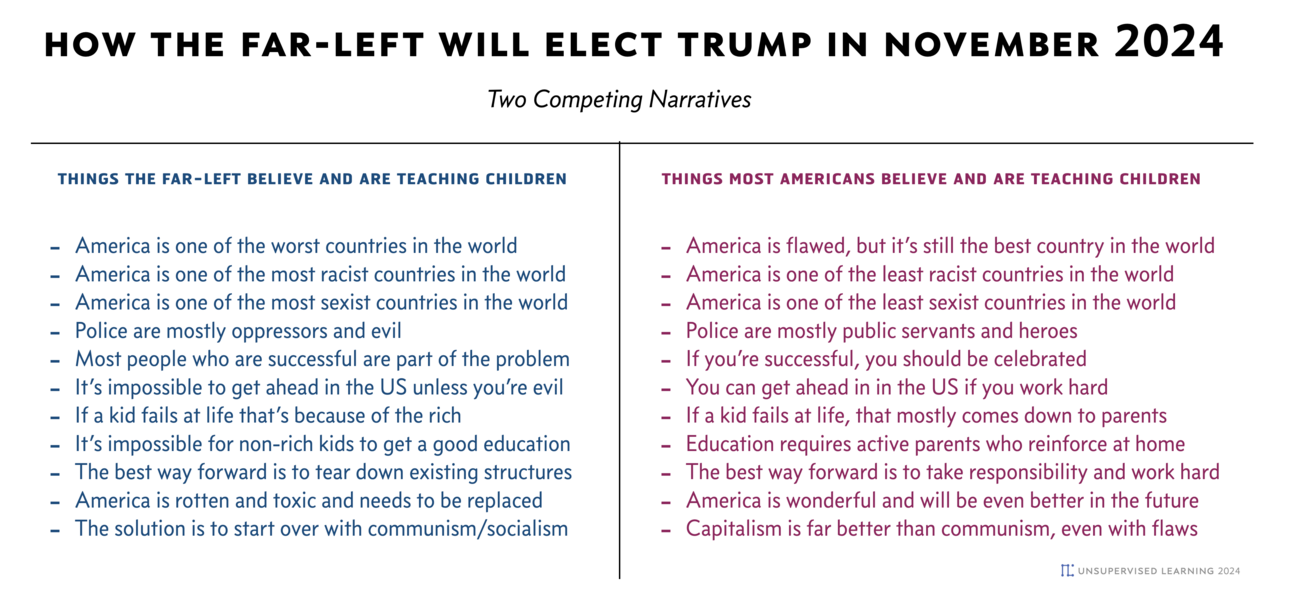
How the Far-left Will Elect Trump in November 2024
Click and read the full-size version before continuing As someone who detests Trump, I think I finally figured out why he’s so popular. In short,…