How Developers Prevent Production Risk at the Source
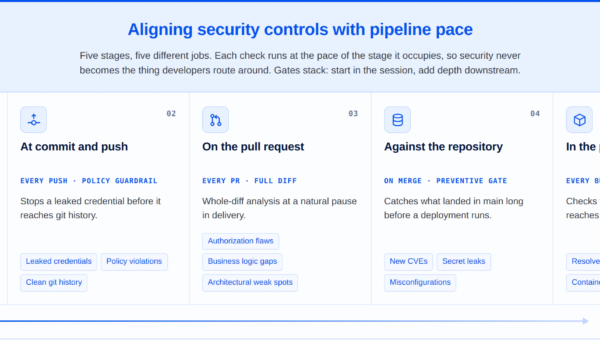
A developer pulls node:20-slim as a base image. It’s a sensible default and what most documentation reaches for. It also ships with 14 known CVEs,…
A developer pulls node:20-slim as a base image. It’s a sensible default and what most documentation reaches for. It also ships with 14 known CVEs,…
Financial services organizations are drowning in data. From emails and Bloomberg chats to WhatsApp messages and calls, the need to review communications data to detect…
Infostealer logs have evolved from an underground commodity into an operational security problem. For defenders, finding an exposed credential is only the beginning. In today’s…
Microsoft will begin expanding memory integrity protection across eligible Windows devices in October 2026, automatically enabling a stronger kernel-level security baseline for more users and…
Cybersecurity researchers at Huntress have uncovered a phishing campaign that abuses Faronics Deploy, a legitimate endpoint management platform used by businesses, schools, and government offices…
Flock tells WIRED that officers cannot run searches using prohibited attributes, including religion and nationality, and that an attempt to search prohibited terms “will be…
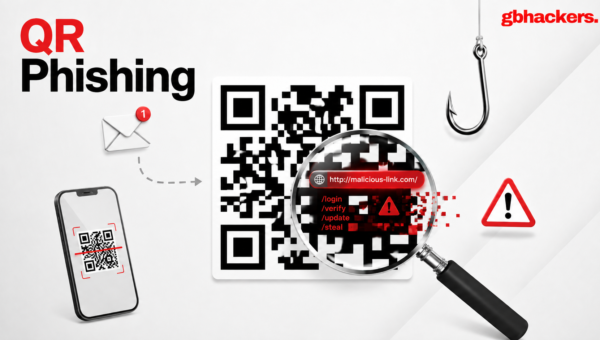
QR code phishing, widely known as “quishing,” has reached record levels as threat actors increasingly conceal malicious URLs within scannable images rather than placing clickable…
A Russian national accused of using fake accounts on a freelance employment platform to spread malware to approximately 80,000 users has been indicted by a…
First, the good news: If you use a Linux-based operating system, you may not be asked your age in a few months. The bad news…
Threat actors are leveraging the trusted Node.js JavaScript runtime in multiple cyber attacks as a way to deploy malicious payloads. According to a new report…
Bug bounty programme operator HackerOne has revealed it has patched a dangerous remote code execution (RCE) vulnerability in its production environment that it would likely…
SonicWall disclosed this week that attackers are chaining two previously unknown vulnerabilities in its SMA1000 secure access appliances to run commands on unpatched devices, and…