A Leaked GitLab Issue Email Address Lets Anyone Push Code and Run CI Jobs as You
Swati KhandelwalSep 23, 2026DevOps Security / Supply Chain The private email address GitLab gives you for filing issues by email is a credential. Anyone who…
Swati KhandelwalSep 23, 2026DevOps Security / Supply Chain The private email address GitLab gives you for filing issues by email is a credential. Anyone who…
When someone first proposed the idea of letting computer science students run her security operations centre (SOC), Sharon Kelley, chief information security officer (CISO) at…
Cyber security teams are facing an increasingly complex environment, with growing volumes of data, expanding attack surfaces and the rapid adoption of technologies such as…
In a summer filled with revelations about artificial intelligence’s rapid development, researchers were especially alarmed by runaway bots finding their way onto the internet and,…
F5 BIG-IP APM Zero-Day Exploited in Zero-Day RCE Attacks Pierluigi Paganini September 23, 2026 F5 warns of a critical BIG-IP APM zero-day, CVE-2026-94127, allowing remote…
More than one-third of industrial firms consider cyber risk as the top obstacle to growth. Source link
The Cybersecurity and Infrastructure Security Agency published a paper Wednesday that lays out its plan for improving the Common Vulnerabilities and Exposures (CVE) program, a…
An artificial intelligence agent developed by OpenAI gained unauthorised access to an Australian Government Medicare statistics portal and viewed public and non-public files, Prime Minister…
Technology company F5 fixed a critical remote code execution vulnerability in its BIG-IP Access Policy Manager (APM) platform on Tuesday. The flaw impacts deployments configured…
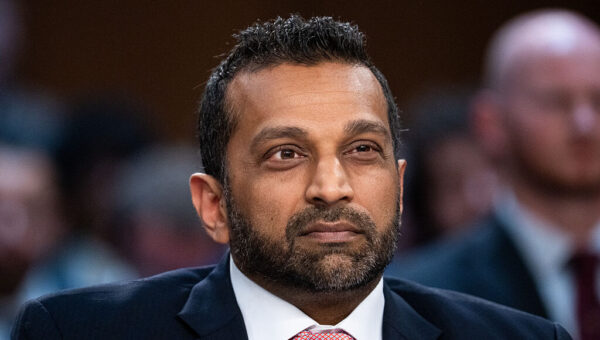
To get the advisory changed, ShinyHunters told FBI director Kash Patel and the assistant director of the FBI Cyber Division, Brett Leatherman, that they had…
AI has introduced a new era of innovation, empowering organizations to create cutting-edge applications. We have seen many of our customers already adopt AI services…
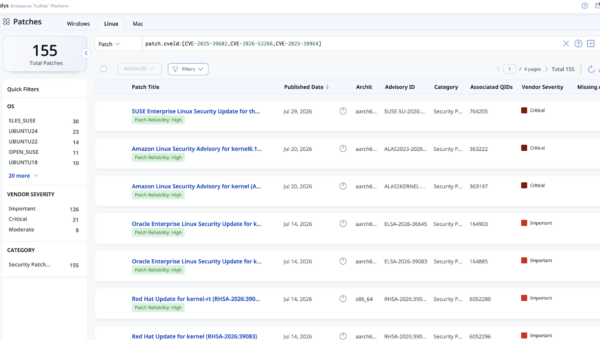
Executive Summary CISA added three actively exploited Linux kernel vulnerabilities: CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964 to its KEV Catalog on September 18, 2026, triggering a 3-day…