Mercor AI Confirms Data Breach Following Lapsus$ Claims of 4TB Data Theft
Mercor AI has officially confirmed a severe data breach following claims by the notorious Lapsus$ hacking group that they stole 4 terabytes of sensitive company…
Mercor AI has officially confirmed a severe data breach following claims by the notorious Lapsus$ hacking group that they stole 4 terabytes of sensitive company…
Last week, DarkSword was then posted to open source code repository GitHub, making it all the more accessible. Security firms Malfors and Proofpoint soon after…
Artificial intelligence agents are transforming enterprise workflows, but they also introduce dangerous new attack vectors. Security researchers from Palo Alto Networks’ Unit 42 recently uncovered…
Generative AI tools have brought the cost of deepfake production low enough that criminals and state-sponsored actors now use them routinely against financial institutions. A…
The cybersecurity landscape is accelerating at an unprecedented rate. What is emerging is not simply a rise in the number of vulnerabilities or tools, but…
After Google moved up its quantum readiness timeline and revealed it was working on building post-quantum cryptography (PQC) features into the next version of its…
Anthropic has sign a memorandum of understanding to share its economic index data with the Australian government to help track artificial intelligence adoption across the…
Attackers hijack Axios npm account to spread RAT malware Pierluigi Paganini March 31, 2026 Threat actors hijacked the npm account of Axios to distribute RAT…
President Donald Trump signed an executive order Tuesday that purports to limit mail-in voting, though critics say the move will almost certainly be challenged in…
The past four weeks have seen a slew of new cybersecurity wake-up calls that showed why every organization needs a well-thought-out cyber-resilience plan 31 Mar…
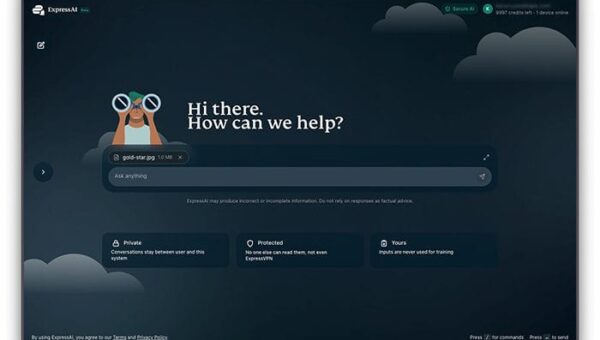
ExpressVPN has launched ExpressAI, a private AI platform it says is designed to let users access AI tools without their prompts and files being used…
“When F5 CVE-2025-53521 first emerged last year as a denial-of-service issue, it didn’t immediately signal urgency, and many system administrators likely prioritized it accordingly,” Benjamin…