Homebrew 7.0.0 gets built-in GUI, better security controls
Homebrew package manager version 7.0.0 has been released with a built-in vulnerability scanner, stronger security controls, and the full release of its native BrewUI graphical…
Homebrew package manager version 7.0.0 has been released with a built-in vulnerability scanner, stronger security controls, and the full release of its native BrewUI graphical…
Container security spans the whole lifecycle build (image scanning, IaC), ship (registry, admission), and run (runtime detection, drift) across modern multi-cloud security architectures. Aqua and…
Threat actors are increasingly weaponizing Microsoft’s Volume Shadow Copy Service (VSS) for two distinct objectives: removing recovery options before ransomware deployment and extracting credential material…
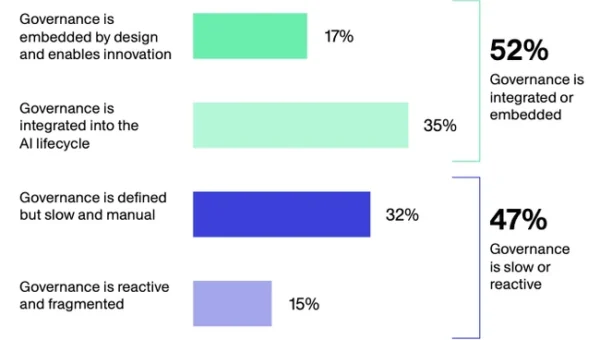
Seventy-four percent of respondents report departmental or scaled AI adoption at their organizations, including within individual teams or departments, across business functions, and as part…
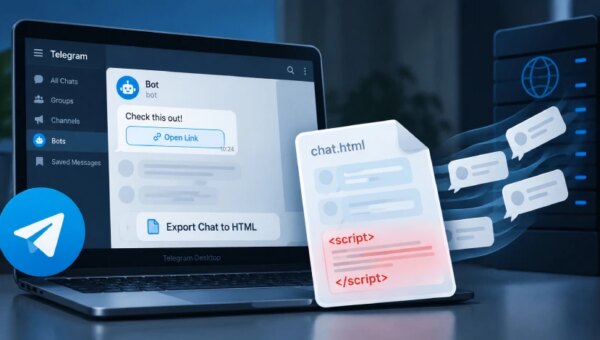
A flaw in Telegram Desktop let a bot’s message plant hidden JavaScript inside chats that users exported to HTML files, security researchers at ExPatch said…
The Finnish government has launched a politically contentious plan to transform the country’s entire public sector into an artificial intelligence (AI)-powered system by 2031. With…
Key points Lina Khan has warned that AI companies have no exemption from existing law over models that disrupt other organisations’ systems. OpenAI has admitted…
A current debate is whether artificial intelligence (AI) is a force for good or bad; or perhaps both. What follows is the argued opinion of…
U.S. CISA adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog Pierluigi Paganini September 14, 2026 U.S. Cybersecurity and Infrastructure Security…
The Supreme Court has rejected a petition by the Trump administration to implement changes to the way the U.S. Postal Service handles mail-in ballots for…
KAIperShield and Cyber in Space have signed a business development and customer engagement agreement aimed at expanding access to cyber resilience and mission assurance capabilities…
Beyond patching, the watchTowr Intel team said defenders should try to identify exploitation attempts by hunting through log files for HTTP POST requests to “/api/v4/projects/{id}/repository/commits/”…