AWS Resolves Major Outage After Nearly 24 Hours of Service Disruption
Amazon Web Services experienced a significant service disruption in its US-EAST-1 region that lasted nearly 24 hours, affecting over 140 services and causing widespread issues…
Amazon Web Services experienced a significant service disruption in its US-EAST-1 region that lasted nearly 24 hours, affecting over 140 services and causing widespread issues…
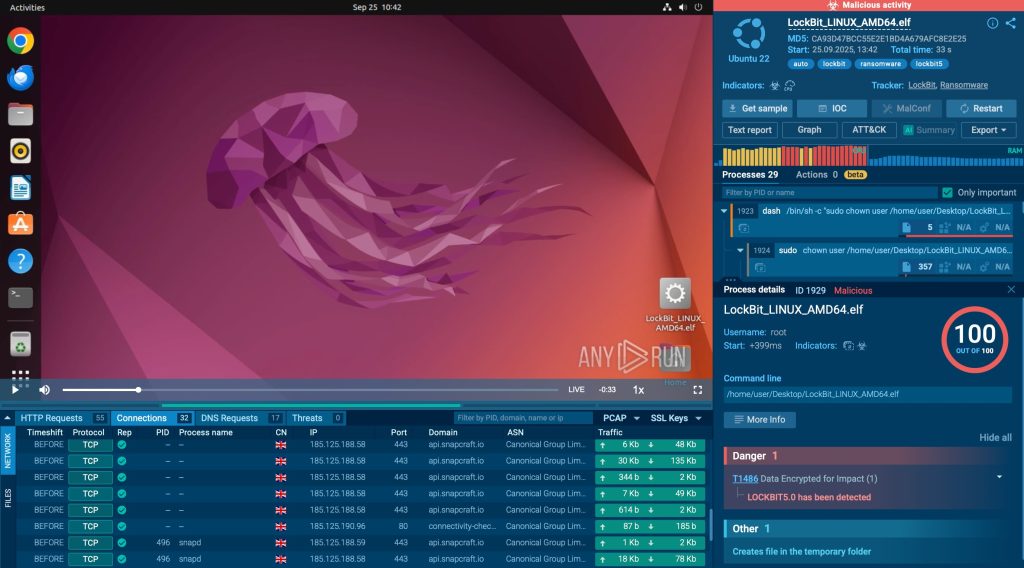
(This post was developed in partnership with researchers from ANY.RUN) Every CISO (or chief information security officer) knows the feeling: endless alerts, constant context switching, and…
A severe vulnerability in the random number generation method of the widely used open-source Bitcoin library Libbitcoin Explorer has led to the exposure of more…
Singapore’s coordinating minister for national security has warned that countries that weaponise technology are fuelling a “cyber arms race”, as officials and experts at a…
A critical security flaw has been found in the on-premise edition of LANSCOPE Endpoint Manager that could let attackers run malicious code on vulnerable machines.…
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert regarding the active exploitation of a high-severity Windows vulnerability, tracked as CVE-2025-33073. This…
Microsoft has released an emergency update to fix the Windows Recovery Environment (WinRE), which became unusable on systems with USB mice and keyboards after installing…
Russian state-sponsored threat actor COLDRIVER, long known for targeting high-profile NGOs, policy advisors, and dissidents, has been linked to a rapidly evolving malware campaign following…
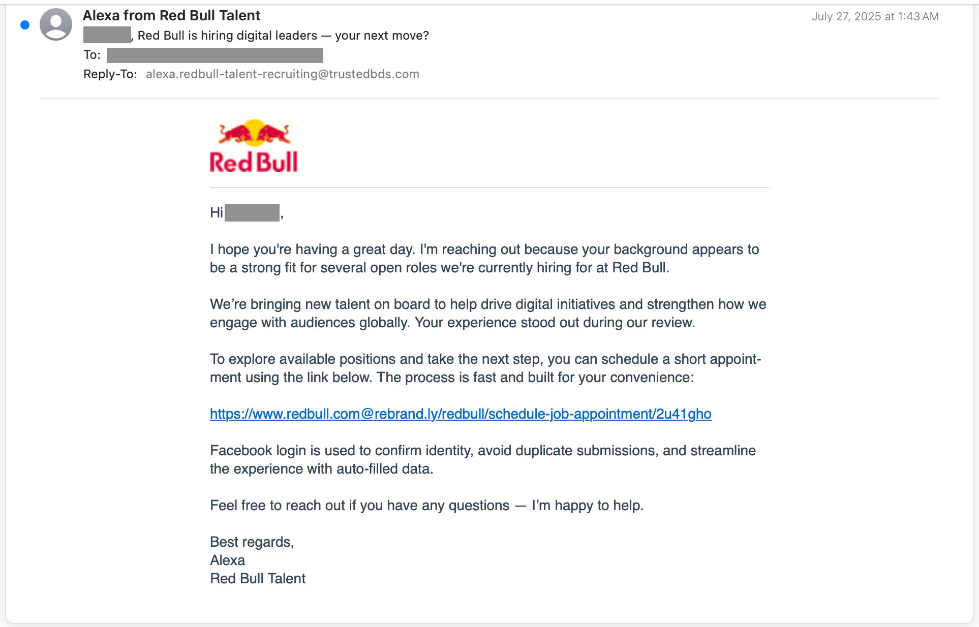
The search for a new job, especially with a slow labour market in the US, has become the perfect opportunity for scammers to trap unsuspecting…
Microsoft has disclosed a serious security flaw in ASP.NET Core that enables authenticated attackers to smuggle HTTP requests and evade critical protections. Tracked as CVE-2025-55315,…
The Cybersecurity and Infrastructure Security Agency (CISA) has added a critical Microsoft Windows Server Message Block (SMB) vulnerability to its Known Exploited Vulnerabilities catalog, warning…
Oct 21, 2025Ravie LakshmananCyber Espionage / Network Security A European telecommunications organization is said to have been targeted by a threat actor that aligns with…