Unsloth’s model picker had a code-execution problem
That’s not necessarily dangerous by itself. Some legitimate Hugging Face models, including IBM Granite Speech and Vision, DeepSeek-OCR, ChatGLM, and earlier Qwen releases, need custom…
That’s not necessarily dangerous by itself. Some legitimate Hugging Face models, including IBM Granite Speech and Vision, DeepSeek-OCR, ChatGLM, and earlier Qwen releases, need custom…
Cyware, vendor of agentic AI-powered operational threat intelligence and collective defense, today announced its partnership with WaterISAC, which serves as the communications and information-sharing organization…
When we launched User Insights last month, we wanted to help teams answer a basic question: What are people actually doing with AI? User Insights…
At Elastic, we believe in the power of open source and understand the importance of community. By putting the community first, we ensure that we…
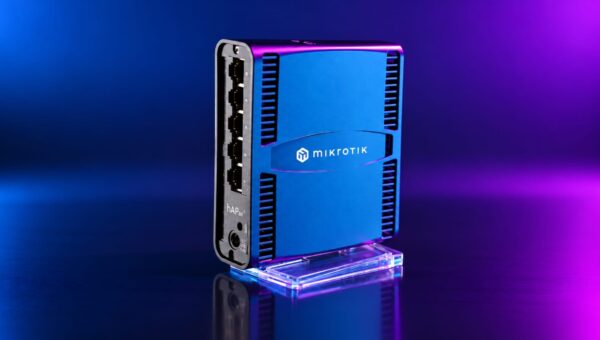
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning of a new critical vulnerability in MikroTik RouterOS that could lead to remote code execution…
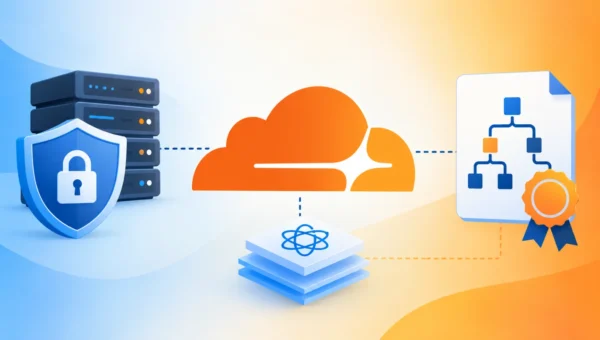
Cloudflare is building a certificate authority to make post-quantum website authentication practical without burdening TLS connections with oversized signatures. The company plans to issue conventional…
Security researchers at Huntress have detailed a multi-stage intrusion in which a threat actor compromised three web servers belonging to a popular recreation management platform…
Russian state-linked threat actor Star Blizzard has expanded its cyberespionage operations in 2026 with a phishing and malware-delivery technique tracked by Microsoft as RedFlick. Microsoft…
A Ransomware-as-a-Service (RaaS) operation known as Global Group is targeting large enterprises with phishing emails that deliver a file-encrypting payload. Research shared with Hackread.com by…
The fifth annual BreachLock Penetration Testing Intelligence Report analyzes 531,770 security findings from 4,970 penetration tests across more than 60 industries, revealing the vulnerabilities, attack…
“Advanced and suspected state-sponsored threat actors” are likely to be behind the initial targeted intrusions that leveraged CVE-2026-88772, one of the two recently disclosed NetScaler…
“Arizona’s court system was targeted by a cyber attack from criminal hackers or their bots.” This is how the Arizona Supreme Court announced that hackers…