
Bypassing a WAF by Finding the Origin IP

Source link
Related Articles
All Mix →
Severe Confluence Vulnerability is an Active Threat (CVE-2022-26134)
Background The vulnerability allows unauthenticated remote code execution (RCE). Exploitation occurs by sending an HTTP request with an attack payload to a vulnerable instance of…
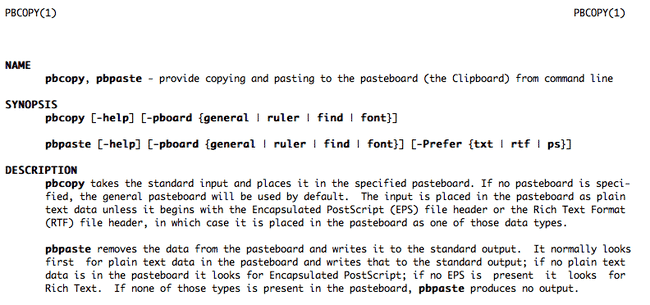
OS X: Manipulating the Clipboard via Command Line
So I somehow just found out that you can manipulate OS X’s clipboard via command line. The utility that does it is called pbcopy (and…

Hack My Career: Advice from HackerOne Employees
Today, we gathered insights from five HackerOne employees offering career advice to illuminate this journey and provide guidance. Kayla Underkoffler, Senior Security Technologist in Pennsylvania,…
Why and How I Believe We’ll Attain AGI by 2025-2028
Table of Contents The key is disparate components talking to each other Looking at the components in detail The intuition What about consciousness? Summary I…
The AI Pentesting wave. Pay for effort vs pay for impact.
For the last year, a version of the same conversation has followed me from customer calls to conference hallways and back into internal meetings. I…
Prompt Injection Attacks and Mitigations · rez0
Table of Contents Why Care? Prompt Injection Attacks Potential Mitigations Thanks and wishes I recently participated as a panelist on a HackerOne press panel where…