CastleStealer, a C# information stealer first publicly identified in April 2026, has expanded its capabilities beyond credential theft.
New samples analyzed by Flashpoint bypass Chromium app-bound encryption, support remote command execution, and transmit stolen data through small, encrypted TCP exchanges instead of uploading a single archive.
Flashpoint has not observed widespread adoption among threat actors. However, the malware’s continuing development, sophisticated loaders, and expanded post-compromise functionality make it an emerging threat rather than a static credential-harvesting tool.
Early CastleStealer activity relied on ClickFix social engineering to deliver a Python script that executed CastleLoader.
By June, attackers had introduced another distribution chain, using malicious advertisements to funnel victims toward fraudulent Node.js installation websites.
A batch script disguised as an installer downloaded and executed OXLOADER, a newer loader incorporating multiple self-decryption stages, obfuscated API resolution, sandbox checks, and in-memory execution.
Flashpoint assesses that these loaders appear to be developed in-house, demonstrating substantial technical proficiency in stealth and anti-analysis.
Flashpoint said in a report shared with GBhackers, the transition illustrates how CastleStealer’s operators are refining both initial delivery and payload capabilities, with loader protections complicating inspection before the stealer begins collecting information.
CastleStealer Malware
On execution, CastleStealer checks the system’s Multilingual User Interface languages for Russian, identified as ru-RU.
It then establishes contact with command-and-control infrastructure, transmitting a handshake containing its build UUID and basic host information before sending additional machine details.
Its Chromium collection routines target saved logins, cookies, browsing history, web data, and browser-extension information. Extension collection includes identifiers, IndexedDB databases, and extension storage.
Firefox targeting covers credentials, cookies, browsing history, and form history. The malware also collects Steam configuration files, including config.vdf, loginusers.vdf, and local.vdf, and searches APPDATA for Discord and Telegram directories.
File harvesting excludes certain file types and filenames containing “backup,” while prioritizing names containing “wallet.”
This collection scope aligns with the broader infostealer threat, which encompasses credentials, browser artifacts, financial information, and cryptocurrency-related data
The most consequential browser-related upgrade is support for bypassing ABE, or app-bound encryption.
Earlier CastleStealer samples could not extract protected data from updated browsers implementing this control.
Newer samples use Chrome’s IElevator COM interface to bypass that protection, a technique Flashpoint notes is also employed by other modern infostealers.
The change removes a previously observed collection limitation; it does not establish that every browser configuration is vulnerable.
CastleStealer also implements a basic remote shell. Operators can submit shell commands, supply files for execution, or provide URLs from which the malware downloads and launches additional payloads.
These functions expand attacker options after initial theft, enabling direct interaction with compromised systems rather than ending activity when collection finishes.
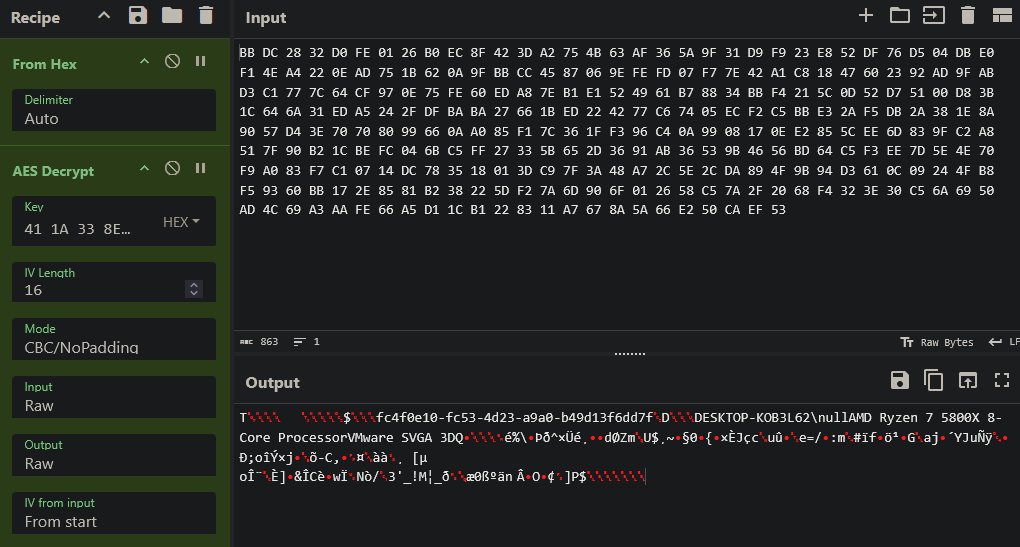
Instead of packaging stolen information into one archive, CastleStealer sends smaller transmissions over raw TCP using AES encryption.
Packets comprise a four-byte size field, an initialization vector, and encrypted data; Flashpoint’s analysis demonstrates AES-128 CBC decryption.
Analysts assess that smaller transfers may reduce conspicuous network-volume spikes, although encryption alone does not make traffic undetectable. After completing its activity, the malware uses a ping-delay technique to delete itself.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.