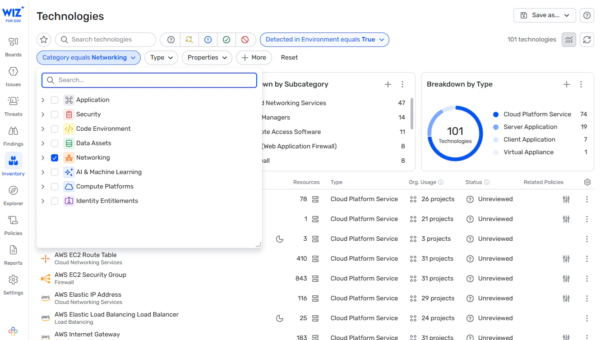
Wiz + Spotify Backstage: Security at the Developer’s Desk
Every developer has a mental map of their services. You know what you own. You know what’s on fire. You know what used to be…
Every developer has a mental map of their services. You know what you own. You know what’s on fire. You know what used to be…
This Red Agent POV focuses on Broken Object-Level Authorization (BOLA), and deep dives into a critical authorization bypass vulnerability discovered in an airline’s GraphQL booking…
Over the last two decades, the enterprise landscape has undergone a massive transformation. Established organizations migrated to the cloud to capture efficiency gains, while a…
The AWS Customer Incident Response Team (AWS CIRT) encounters patterns that repeat across engagements when helping customers respond to security incidents. We’re passionate about making…
Digital transformation across the U.S. Public Sector has reached a pragmatic milestone. To accelerate mission delivery, federal, state, and local agencies are actively operating within…
We are excited to launch the AI Cyber Model Arena. This work introduces a benchmark suite of 257 real-world challenges spanning five offensive domains: zero-day…
In the world of government compliance, ‘fast’ isn’t usually a word thrown around lightly. Historically, taking a product from ‘Ready’ to ‘Authorized’ in the FedRAMP…
Five years after Log4Shell, the industry faced another critical RCE, this time in the React and Next.js ecosystems. Nearly 40% of cloud environments were affected…
Cloud fundamentally changed the way we build and maintain software, and AI is changing everything again. Development cycles have accelerated from months to minutes. Cloud…
The Shift from “Periodic” to “Continuous” In the first part of our FedRAMP series, we explored Wiz’s accelerated journey to FedRAMP High. However, seasoned CSPs…
In the era of AI-driven development, the cloud attack surface is expanding faster than traditional security operations can reasonably keep up. Cloud environments evolve continuously,…
Cloud-native and AI-driven development keep accelerating, and security needs to move just as fast. As application security moves from siloed scanners to continuous exposure management,…