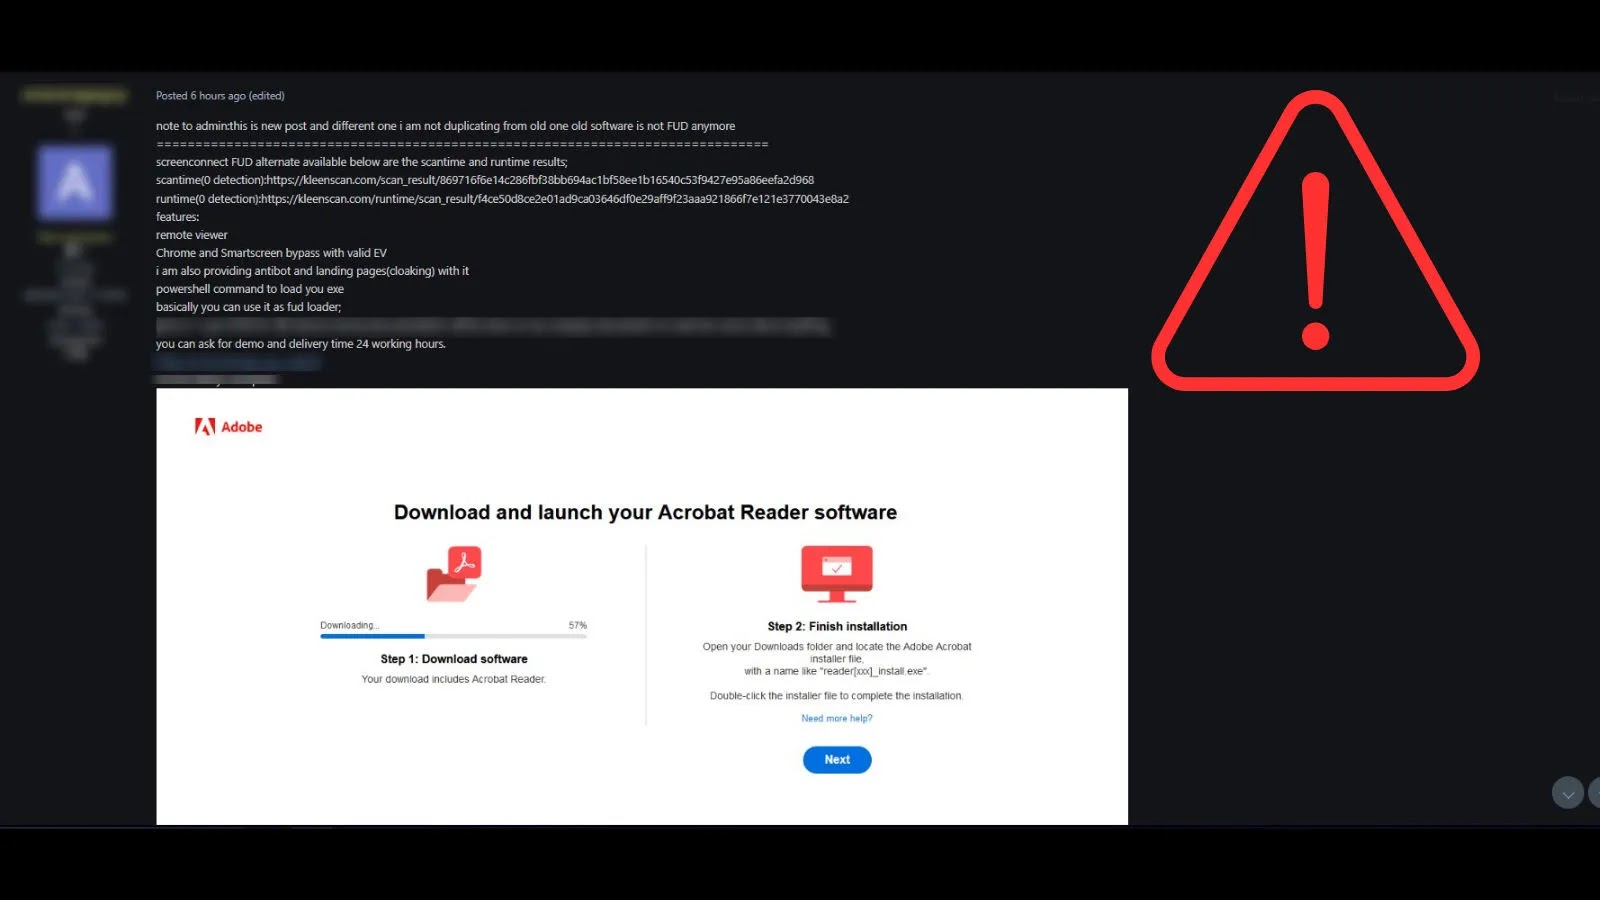
Threat Actors Selling New Undetectable RAT As ’ScreenConnect FUD Alternative’
A threat actor has been observed advertising a new Remote Access Trojan (RAT) on underground forums, marketing it as a fully undetectable (FUD) alternative to…
A threat actor has been observed advertising a new Remote Access Trojan (RAT) on underground forums, marketing it as a fully undetectable (FUD) alternative to…
Cybersecurity researchers have identified a potential connection between two Yemen-based cybercriminal organizations, the Belsen Group and ZeroSevenGroup, following an extensive investigation into their operational patterns…
In early 2025, cybersecurity researchers observed an unprecedented collaboration between two Russian APT groups targeting Ukrainian organizations. Historically, Gamaredon has focused on broad spear-phishing campaigns…
Phishing campaigns have long relied on social engineering to dupe unsuspecting users, but recent developments have elevated these attacks to a new level of sophistication.…
A critical authentication bypass vulnerability has emerged in Nokia’s CloudBand Infrastructure Software (CBIS) and Nokia Container Service (NCS) Manager API, designated as CVE-2023-49564. This high-severity…
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a critical warning regarding sophisticated malware campaigns targeting Ivanti Endpoint Manager Mobile (EPMM) systems. Cybercriminals are…
The emergence of a new campaign weaponizing legitimate remote monitoring and management software has alarmed security teams worldwide. Attackers are distributing trojanized installers for ConnectWise…
ChatGPT agents can be manipulated into bypassing their own safety protocols to solve CAPTCHA, raising significant concerns about the robustness of both AI guardrails and…
The emergence of the SystemBC botnet marks a significant evolution in proxy-based criminal infrastructure. Rather than co-opt residential devices for proxying, SystemBC operators have shifted…
Remote Desktop Protocol (RDP) and Secure Shell (SSH) have changed how organizations manage their IT systems. These tools allow employees to access and control their…
A newly disclosed flaw in HubSpot’s open-source Jinjava template engine could allow attackers to bypass sandbox restrictions and achieve remote code execution (RCE) on thousands…
A deserialization flaw in the License Servlet component of Fortra GoAnywhere Managed File Transfer (MFT) platform. Identified as CVE-2025-10035, this vulnerability permits an unauthenticated attacker…