FBI arrests Cypfer co-founder Edward Dubrovsky, now associated with CyberSteward, in the ShinyHunters investigation into the FBI jobs portal breach.
A co-founder of Canadian ransomware negotiation firm Cypfer has been identified as the person arrested in connection with the FBI’s ShinyHunters investigation, adding an unexpected turn to a case already involving suspected hackers, breached FBI systems and international arrests.
The New York Times reported on October 9 that the FBI had arrested a suspect in Pennsylvania connected to the ShinyHunters investigation. Cybersecurity journalist Brian Krebs later identified the suspect as Edward Dubrovsky, a Canadian cybersecurity executive and co-founder of Cypfer. Krebs reported that Dubrovsky is now associated with another Canadian security firm, CyberSteward.
Dubrovsky is not an unknown figure in cybersecurity. His professional background is in ransomware negotiation and incident response, work normally associated with helping companies respond to extortion attacks.
The arrest also comes days after a separate DOJ case against MonsterCloud CEO Zohar Pinhasi, another ransomware recovery figure accused of secretly paying attackers for decryption keys while charging victims higher recovery fees. The two cases are separate, but both put new scrutiny on companies and individuals working around ransomware recovery and negotiation.
The FBI has not publicly released Dubrovsky’s name in a formal announcement reviewed by Hackread.com. The exact charges, if any, and his alleged role in the ShinyHunters investigation were not immediately clear at the time of writing.
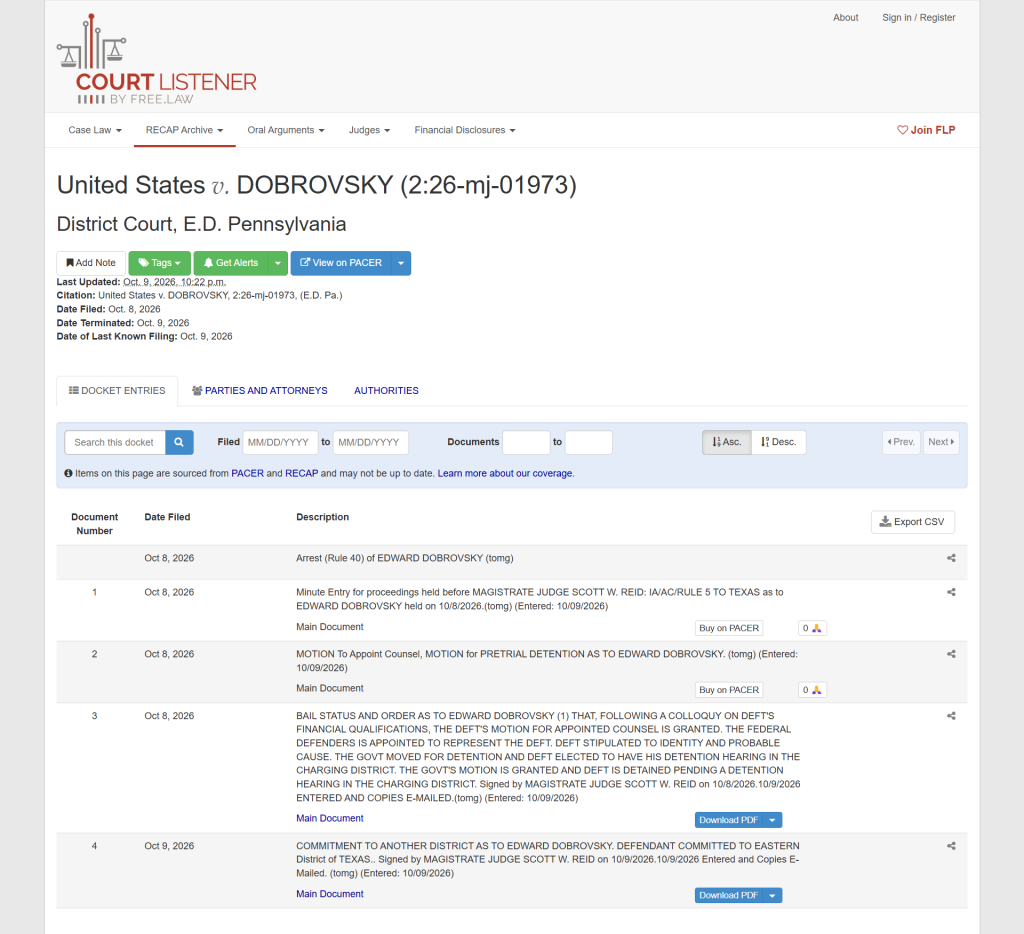
Court records reviewed by Hackread.com show the case was filed in the Eastern District of Pennsylvania on October 8 and terminated there on October 9 after Dubrovsky was committed to the Eastern District of Texas. A bail status order says the government moved for detention, the motion was granted, and Dubrovsky was detained pending a detention hearing in the charging district.
New Arrest Follows Rey Detention
The reported arrest follows earlier coverage of suspected ShinyHunters member Saif al-Din Khader, known online as “Rey,” who was detained in Jordan on September 29. Reuters reported that Khader was cooperating with the FBI and other authorities as investigators worked to identify others connected to the group.
Hackread.com also reported that the FBI confirmed multiple arrests in the ShinyHunters investigation, but declined to identify all suspects or confirm whether Khader was among them. At the time, the bureau said it was working with international partners and continuing to pursue people involved in the cyber incident.
The FBI’s investigation intensified after ShinyHunters claimed responsibility for compromising the FBI’s job application portal (apply.fbijobs.gov).
The group claimed it accessed sensitive information belonging to current, former and prospective FBI personnel, including personal and health-related data. Days later, ShinyHunters told Hackread.com that it will not leak the stolen FBI data and that the breach was part of its marketing campaign.
The FBI confirmed unauthorized activity affecting the jobs portal but has not publicly verified ShinyHunters’ full claims about the stolen data.
PeopleSoft Breach and Contractor Fallout
The FBI jobs portal incident has also led to fallout around third-party system management. A missed security patch reportedly left the bureau’s Oracle PeopleSoft jobs portal exposed, leading the FBI to remove a contractor from its assignment. Accenture was identified as the company managing the platform.
ShinyHunters previously claimed it exploited a PeopleSoft vulnerability to gain access. Google’s Mandiant separately reported that the group had exploited CVE-2026-35273, a critical flaw in Oracle PeopleSoft’s Environment Management component, and used URL encoding to get around WAF rules blocking the vulnerable endpoint.
The newly reported arrest adds another piece to a fast-moving investigation, but several details remain unresolved. Authorities have not publicly explained how Dubrovsky is allegedly connected to the case, whether the arrest is directly related to the FBIJobs.gov breach, or how it fits with the reported detention of Rey and the earlier arrest of Pepijn van der Stap in the Netherlands, the FBI described as an alleged ShinyHunters leader.
For now, the confirmed picture is that the FBI’s ShinyHunters investigation has moved from breach response into arrests, international cooperation and questions about how a missed enterprise software patch exposed one of the bureau’s own systems.
ShinyHunters Data Breach Download Infrastructure Still Intact and Online
Despite the arrests and reported cooperation of suspected members, ShinyHunters’ stolen-data download infrastructure remains active. The group’s dark web leak site has moved in and out of availability in recent days, but its download system is still reachable, with multiple terabytes of stolen data from major companies still available.
The situation leaves an open question for investigators and victims. If Rey was operating or helping manage the platform, the continued availability of the download infrastructure may suggest that other people still have access, that parts of the system were separately hosted, or that the backend was not immediately affected by the arrests. None of those possibilities has been confirmed.