IDScan confirms breach after 153 million driver’s licenses leak on dark web
Days after reports linked IDScan to a dark web database holding more than 153 million driver’s license scans, the identity verification company has confirmed hackers…
Days after reports linked IDScan to a dark web database holding more than 153 million driver’s license scans, the identity verification company has confirmed hackers…
A threat actor built a working exploit for PaperCut print management software, then handed the job of breaking into hundreds of organizations to AI agents…
Researchers at Michigan State University and three partner schools bought a Samsung Galaxy Z Fold 7, copied the identification number printed on the sealed box,…
State-sponsored and financially-motivated attackers are actively exploiting CVE-2026-20079, a critical authentication bypass vulnerability in Cisco Secure Firewall Management Center (FMC), which is used for centrally…
Google turned on a transfer feature in Android that moves passwords and passkeys straight from one password manager to another, with no file to download…
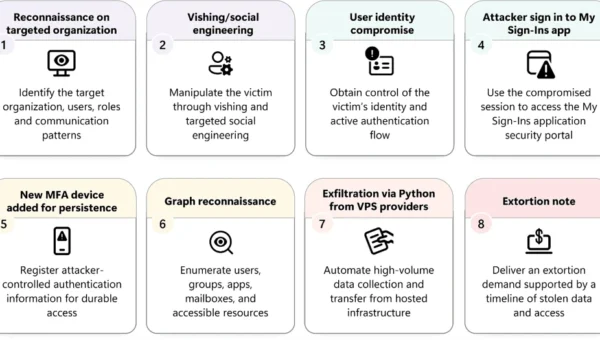
Attackers are calling or texting employees on their personal phones, posing as internal IT staff, in a social engineering campaign that tricks them into handing…
Scytale has announced the launch of their latest AI-powered third-party risk management (TPRM) capabilities within its Vendors module. The release further extends vendor risk management…
Credential harvesting on developer machines has widened. Earlier infostealers worked from a short list of known targets, mostly browser stores and a few cloud credential…
The OpenSSL project released the first alpha of OpenSSL 4.1.0, giving developers an early look at a version built for encrypted communication over unreliable connections…
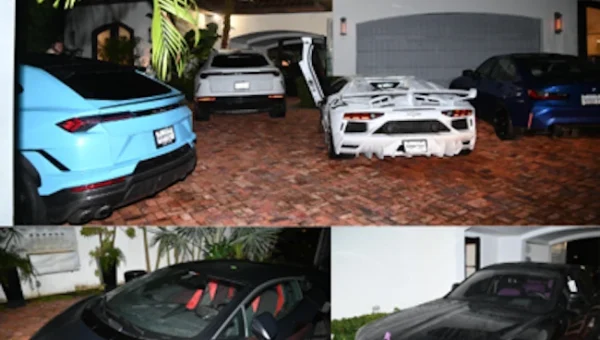
A 22-year-old man built his fortune by breaking into strangers’ digital wallets, then spent it on nightclub tabs, private jets, and a fleet of cars…
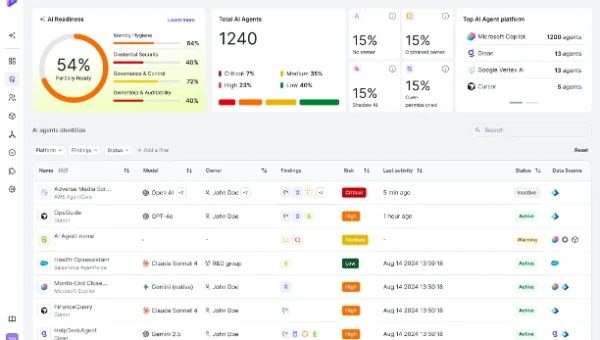
Orchid Security has announced identity drift detection and application-level kill switches for AI agents. They can complete authorized objectives beyond their initial privilege level within…
A rootkit found on hacked F5 BIG-IP APM devices skips the usual step of writing a web shell to disk, hiding it in memory instead,…