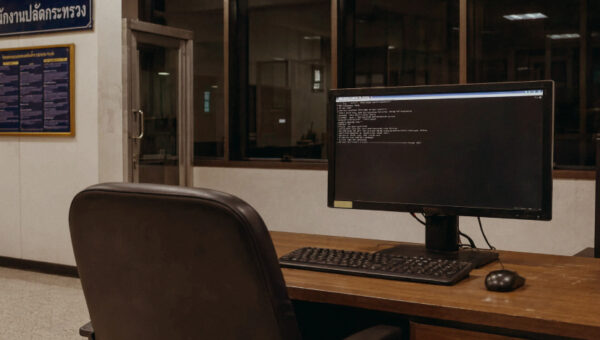
Hacker Runs Hermes AI Agent Unattended for Post-Exploitation at Thai Finance Ministry
Someone installed a popular AI assistant on a rented server, switched off the setting that makes it ask permission before running risky commands, and pointed…
Someone installed a popular AI assistant on a rented server, switched off the setting that makes it ask permission before running risky commands, and pointed…
AI agent security is moving through a familiar maturity curve: adoption, then visibility, and finally, control. But what we’ve collectively discovered is that enforcing least…
The operators of the DevMan ransomware-as-a-service (RaaS) scheme are maintaining a dedicated web platform that offers affiliates the ability to build payloads, oversee earnings, and…
Ravie LakshmananJul 25, 2026Vulnerability / Ransomware Threat actors linked to the Cl0p (aka Chubby Scorpius, FIN11, Graceful Spider, and Lace Tempest) ransomware campaign are exploiting flaws…
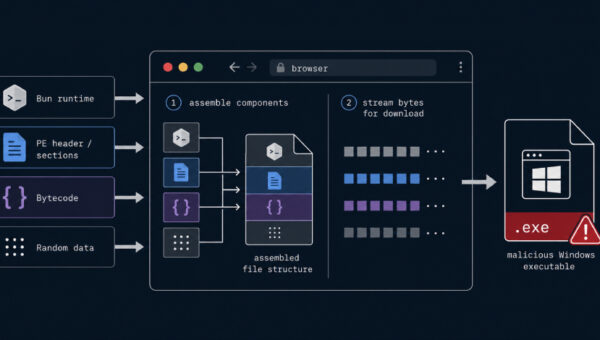
A malvertising operation dubbed SourTrade is making victims’ browsers build the final Windows executable themselves, using a legitimate Bun runtime as its base instead of…
For years, phishing campaigns targeting financial institutions followed the same playbook. Victims were tricked into entering usernames and passwords, attackers collected the credentials, and accounts…
Swati KhandelwalJul 25, 2026Vulnerability / Application Security Security firms ThreatBook and Imperva say attackers are targeting a critical flaw in Fastjson, Alibaba’s JSON library for…
Swati KhandelwalJul 25, 2026Vulnerability / Application Security Security researchers at depthfirst published working exploit code on July 24 for a GitLab flaw that GitLab patched…
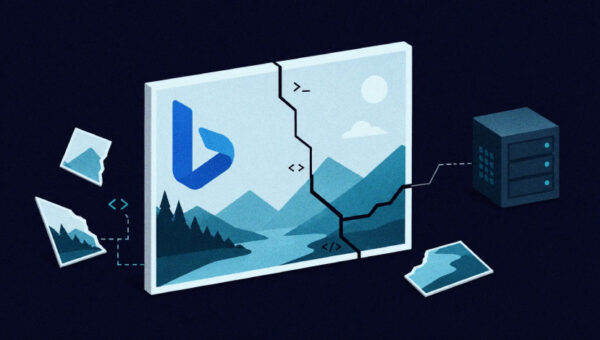
A crafted SVG submitted to Bing’s image search ran commands as NT AUTHORITYSYSTEM on Microsoft’s production image-processing workers, and as root on the Linux machines…
Cybersecurity researchers have disclosed a critical vulnerability in OpenAI’s ChatGPT Workspace Agents that could have allowed a single phishing link to stealthily build, authorize, and…
The North Korean threat actors behind the ClickFix-style campaigns that employ typosquatted Zoom and Microsoft Teams domains have been found to operate an active phishing…
Swati KhandelwalJul 24, 2026Vulnerability / Enterprise Security Researchers H0j3n and Aniq Fakhrul published a working exploit on July 24 that lets a low-privileged Active Directory…