NIST Scales Back NVD CVE Enrichment: What to Know
NIST’s shift toward selective CVE enrichment creates significant visibility gaps for teams relying solely on the National Vulnerability Database. As AI accelerates vulnerability disclosure rates,…
NIST’s shift toward selective CVE enrichment creates significant visibility gaps for teams relying solely on the National Vulnerability Database. As AI accelerates vulnerability disclosure rates,…
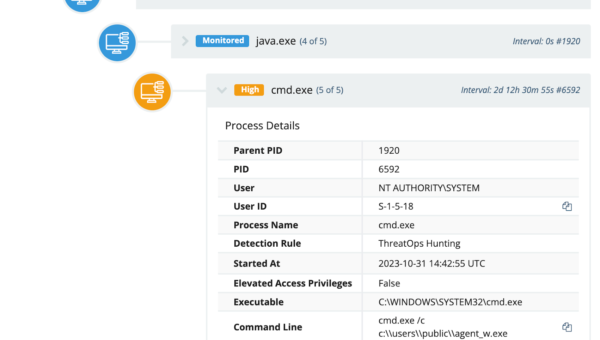
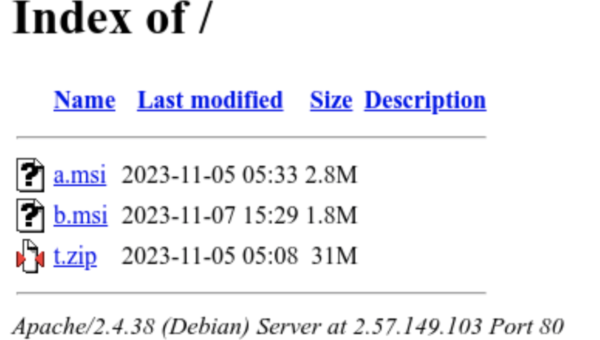
A partner recently deployed Huntress agents on October 30, 2023, after experiencing a “HelloKitty” ransomware attack on October 27. This ransomware attack followed closely with…
On October 31, 2023, Atlassian published patches and an advisory for CVE-2023-22518, an improper authorization vulnerability affecting Confluence Data Center and Confluence Server. Later, on…
In a concerning development within the healthcare sector, Huntress has identified a series of unauthorized access that signifies internal reconnaissance and preparation for additional threat…
On November 8, 2023, SysAid published an advisory expressing that their on-premise server software had a previously undisclosed vulnerability and is aware of public in-the-wild…
Small and medium-sized businesses (SMBs) often find themselves in the crosshairs of today’s cybercriminals. While the spotlight often shines on high-profile breaches affecting corporate giants,…
During the various phases of an attack, it’s not uncommon for threat actors to use “living off the land” binaries (LOLBins) or scripts and libraries…
Threat actors of varying types continue to target managed file transfer (MFT) applications for exploitation. The latest concerning MFT vulnerability was identified by Converge Technology…
In a recent episode of Tradecraft Tuesday, I was joined by Patrick Wardle, Founder of Objective-See Foundation, to talk all about how macOS malware is…
CIS Controls Security Awareness Training The CIS Controls require organizations to implement a security awareness training program as part of Control 14. Huntress’ fun security…
Over the last year, we’ve worked our asses off to prepare for an inbound tidal wave of identity-focused tradecraft. Considering our partners’ significant investments in…
In the realm of cyber threat intelligence (CTI), technical indicators, commonly known as “indicators of compromise” (IOCs), play a pivotal role. Indicators feature prominently in…