Orienting Intelligence Requirements to the Small Business Space
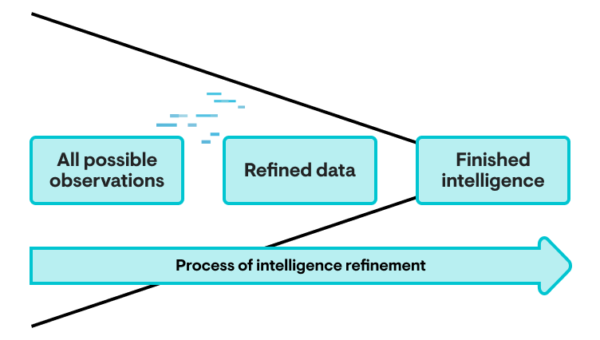
The discipline of intelligence, particularly in the context of cyber operations, features a number of formal concepts and processes that may appear distracting or irrelevant…
The discipline of intelligence, particularly in the context of cyber operations, features a number of formal concepts and processes that may appear distracting or irrelevant…
Security awareness training is easy to think about as a passive item. You go buy a training platform or SCORM files for your LMS, assign…
We’re thrilled to unveil the latest addition to Huntress Managed Security Awareness Training: Managed Phishing! Over the past year, we’ve worked tirelessly to shape Huntress…
The challenges of 2025, tight budgets, rising AI anxiety, and increasingly organized cybercrime, didn’t go away. They matured. The threat landscape of 2026 is sharper,…
There was once honor among thieves. When it came to cyber threats, hackers considered the healthcare industry as the “untouchable” sector, shielded by an unspoken…
In a world of many noisy tools, Huntress has always been mindful of how real people are fighting against cyberattacks every day. Our goal is…
In today’s world, IT operations are becoming more and more decentralized. And this shift makes things particularly complicated for those in the healthcare sector, like…
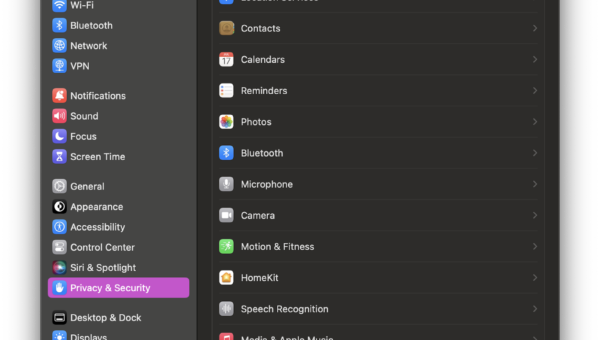
Apple’s commitment to user privacy is well known. One of the key components of their privacy controls is the Transparency Consent and Control (TCC) framework.…
Highlights from March Coming in at number 1 on this month’s top 10 most prevalent threat list is activity related to March 2026’s axios npm…
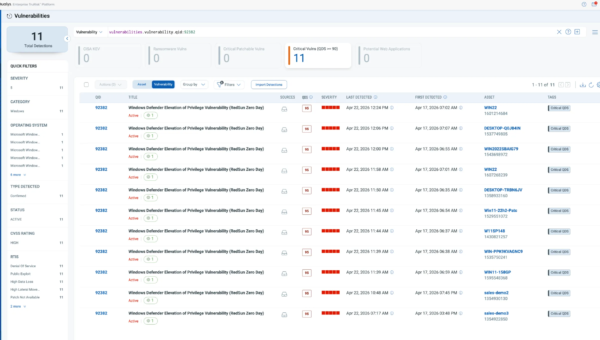
Key Takeaways RedSun is a critical zero-day vulnerability in Microsoft Defender that allows low-privileged users to gain SYSTEM access No patch is currently available, leaving…
Huntress SOC analysts recently alerted customers regarding two disparate endpoints identified as being minimally impacted by ransomware; that is, only a limited number of ransomware…
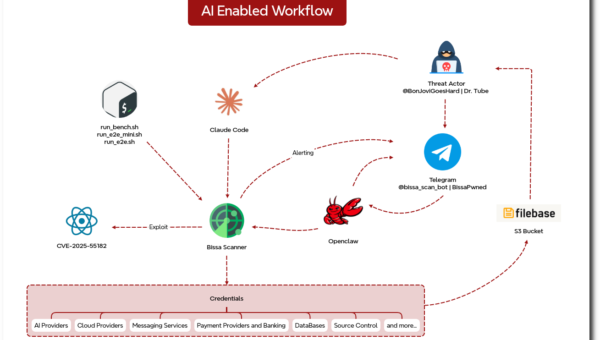
Key Takeaways We recently discovered an exposed server that was used for multi-victim exploitation, staging, review, and validation. Claude Code and OpenClaw were used as…