The Crown Prince, Nezha: A New Tool Favored by China-Nexus Threat Actors
Update: 10/15/25 @ 1pm ET An anonymous individual from Mainland China who is said to be familiar with the activity, detailed here, reached out to…
Update: 10/15/25 @ 1pm ET An anonymous individual from Mainland China who is said to be familiar with the activity, detailed here, reached out to…
Update: 10/15/25 @ 1pm ET An anonymous individual from Mainland China who is said to be familiar with the activity, detailed here, reached out to…
8Critical 75Important 0Moderate 0Low Microsoft addresses 83 CVEs including two vulnerabilities that were publicly disclosed prior to a patch being released. Microsoft patched 83 CVEs…
8Critical 75Important 0Moderate 0Low Microsoft addresses 83 CVEs including two vulnerabilities that were publicly disclosed prior to a patch being released. Microsoft patched 83 CVEs…
“This isn’t just compliance…it’s a national security imperative.” Stacy Bostjanick Chief DIB Cybersecurity, DCIO(CS), OCIO The wait is over. On September 10, 2025, the Department…
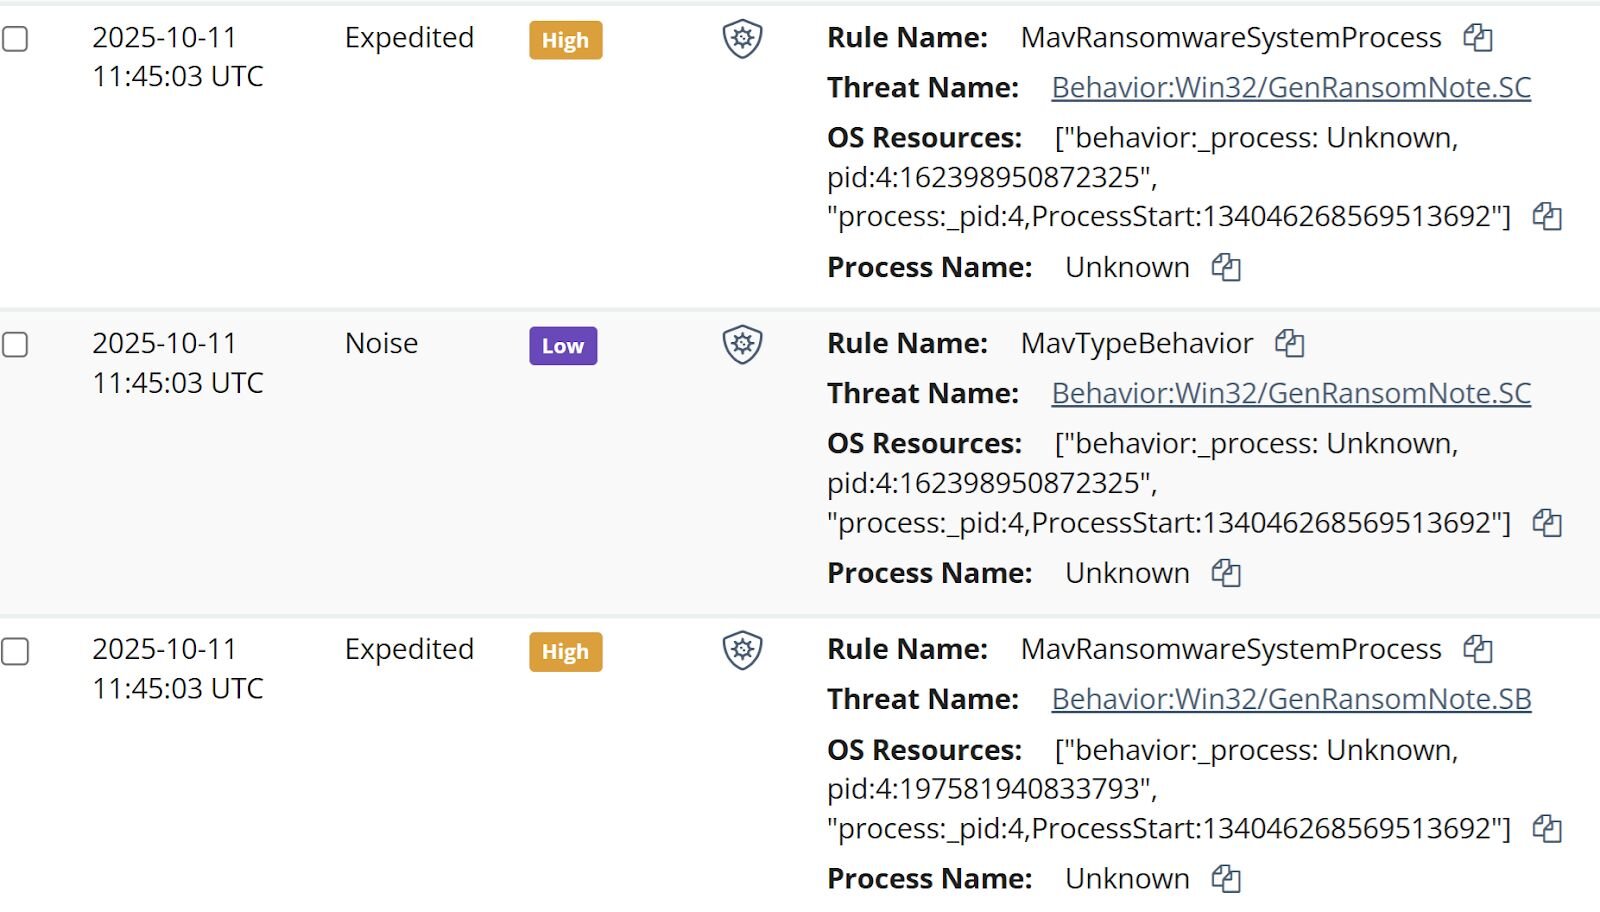
When a ransomware attack occurs, the focus is most often on the encryption of files. Initial access is often glossed over or simply assumed. In…
Another year and yet another RSAC Conference looms. While there are a few invite-only events on Sunday, this year’s conference starts in earnest on Monday,…
Key Takeaways AI security demands a paradigm shift, treating models, endpoints, and integrations as dynamic attack surfaces requiring continuous governance. Inventory-driven visibility is foundational to…
We’ve all seen threat reports and intrusion write-ups that look deeply polished, with a cohesive timeline that highlights incredible telemetry and analysis skills. Cool diagrams…
A big part of a security analyst’s everyday role is figuring out what actually happened during an incident. We can do that by piecing together…
What we built Our team at DEFCERT collaborated with the team at Huntress to build resources that partners and “Organizations Seeking Assessment” (OSAs) can use…
Imagine this: you’re a hacker, and you’re working through an executable file made up of a compiled AutoIT script. You’ve decompiled the script (thanks to…