Proactive Threat Hunting with Elastic Security — Elastic Security Labs
When a new threat actor technique emerges — whether from a research blog, an intelligence feed, or breaking news — every threat hunter instinctively shifts…
When a new threat actor technique emerges — whether from a research blog, an intelligence feed, or breaking news — every threat hunter instinctively shifts…
In the world of Security Operations Centers (SOCs), data is valuable, but excessive data can be problematic. Collecting every single event from every endpoint is…
Discovery: The foundation of exposure management To understand your attack surface, and all related exposures, Rapid7’s Command Platform provides Attack Surface Management, (included in Surface…
SOC leaders face a daily battle against basic math that doesn’t add up. Data volumes are growing exponentially, attack surfaces are expanding globally, yet your…
Let’s talk about Shelby. Shelby runs a successful online artisanal soap store, priding herself on quality and attention to detail. So when an email lands…
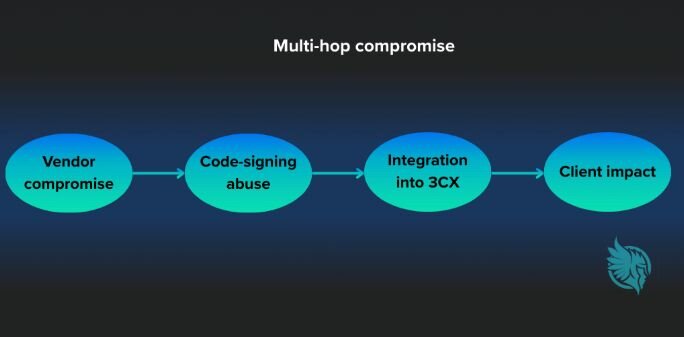
Cybersecurity has always relied on trust. Every software update, hardware purchase, and cloud integration depends on the implicit belief that vendors will protect their customers.…
Migrating to a new SIEM is often viewed as a daunting task. The sheer volume of legacy detection rules, dashboards, and custom configurations can keep…
Introduction: The Need for a Scalable, Automated Simulation Range In modern security operations, detection engineering is no longer a “set it and forget it” discipline.…
Summary On December 29, 2025, a coordinated campaign of destructive cyberattacks targeted Poland’s energy infrastructure, affecting over 30 renewable energy facilities and a major combined…
Summary On February 6, 2026, Microsoft reported the exploitation of SolarWinds Web Help Desk (WHD) servers The exploitation facilitated multi-stage intrusions leveraging remote monitoring and…
Every security professional knows the drill. You go home for the holidays and, without volunteering, you become the family’s help desk, incident responder, and fraud…
Special thanks to Austin Worline for his contributions to this blog post. The Huntress Security Operations Center (SOC) frequently comes across incidents involving rogue ScreenConnect…