A China-aligned espionage group abused the update traffic of Sogou Input Method, one of China’s most widely used keyboard apps, to quietly install the DarkVigil implant on victims’ machines.
ESET Research, which tracks the actor as SlippyNunchucks, published its findings on November 4, 2026. Tencent, which owns Sogou, has patched the flaw in version 16.10.
From July 1, 2026, victims in Hong Kong, Thailand, Japan, Vietnam, Sri Lanka, and Oman received DarkVigil while using the keyboard. The geographic spread first suggested an exploit.
ESET instead found DNS hijacking that abused the app’s use of unencrypted HTTP. Where the DNS manipulation happens is still unknown. ESET suspects compromised routers or interception at the ISP level.
The group has been active since at least September 2023. DarkVigil, also known as FDMTP, is a modular .NET toolset with more than 20 plugins, built on the TouchSocket framework.
Trend Micro first documented FDMTP in 2024 as a secondary control tool used by Earth Preta, also called Mustang Panda. ESET rejects that link and reports no overlap with Mustang Panda.
Notable victims include a gambling operator in Sri Lanka, the Philippines and Hong Kong, an Internet café in Dubai, and a student in Denmark. ESET says the gambling targeting fits Beijing’s crackdown on Southeast Asian scam syndicates.
DarkVigil Malware Campaign
The Sogou component SGTool.exe requests a configuration from config.pinyin.sogou[.]com/api/brandScd/getBrandScd.php.
The request belongs to the app’s brand-vocabulary promotion feature, which fetches icons such as the green sprout badge. ESET found 20 endpoints on that host that the app reaches over plain HTTP, even though the domain supports HTTPS.
On victim networks, the attacker resolved the domain to staging servers at 47.239.250[.]102 or 47.237.122[.]175. Those servers returned a forged AES-encrypted configuration with altered MD5 values, so the integrity check passed.
The configuration told SGTool.exe to download two files from sogou-cdn[.]com. One was a legitimate, signed Adobe Licensing WF Helper renamed biz_helper.exe. The other was the malicious libcef.dll.
The payloads were placed so that Sogou’s own workflows would run them. In one path, the Adobe binary replaces SogouComMgr.exe, so any component install or load launches it and side-loads the DLL.
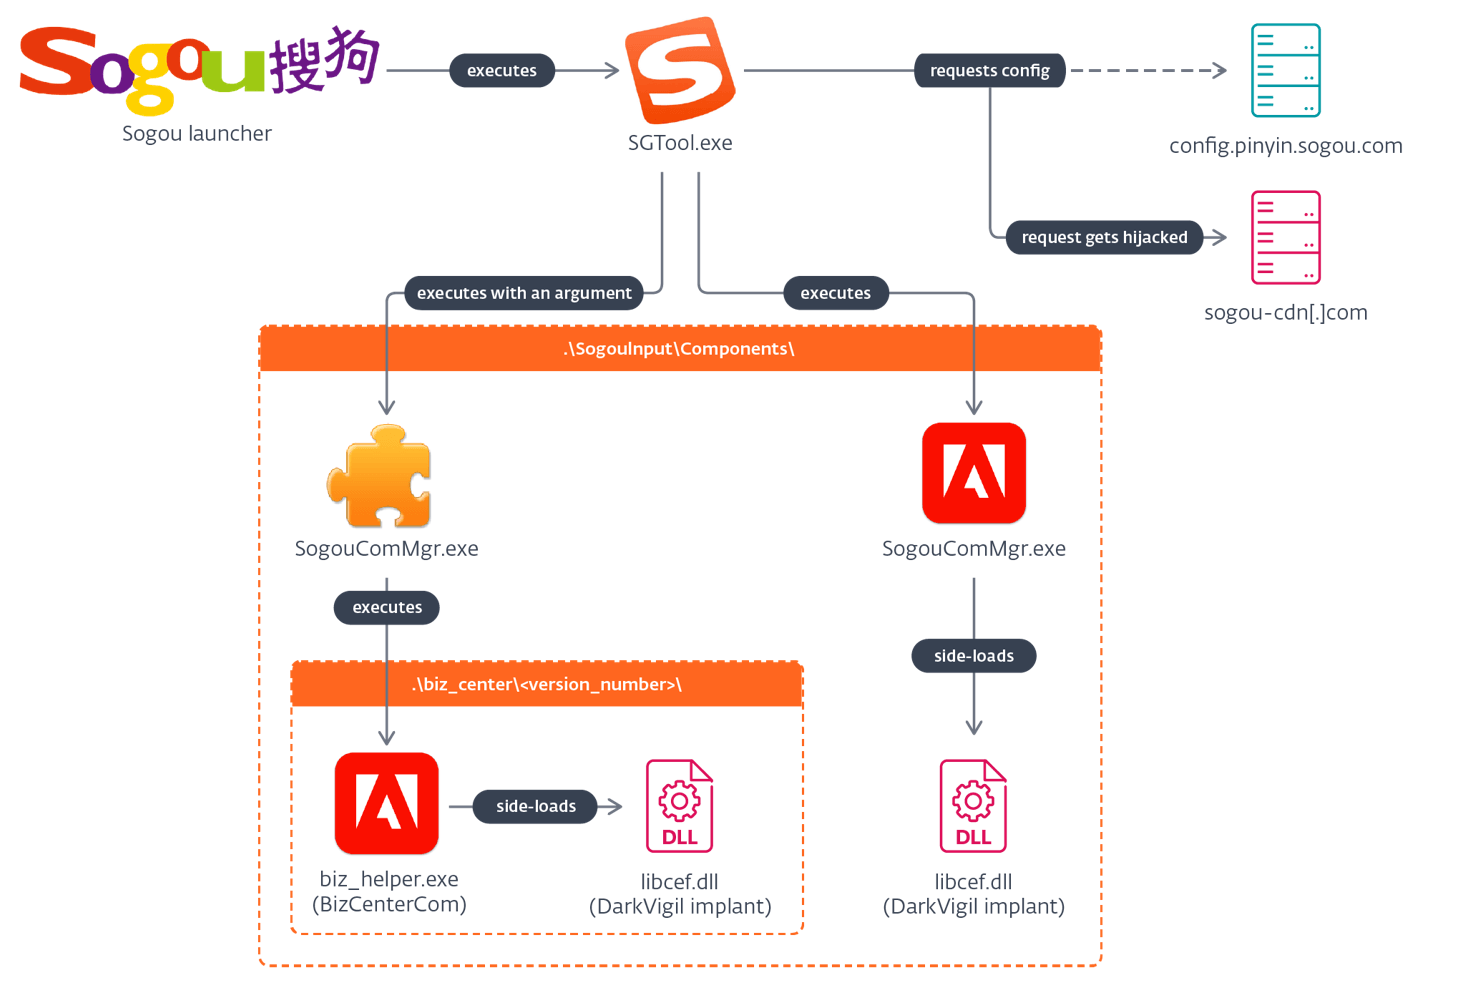
In the other, the files sit in the biz_center directory and run when the BizCenterCom component loads. The attacker needs no separate persistence mechanism, though ESET notes that either method can crash the software.
ESET Researchers said that, DarkVigil communicates over the Duplex Message Transport Protocol (DMTP), which can run over TCP, UDP, HTTP, WebSocket or named pipes.
Its reverse remote procedure call design lets the server and implant invoke each other’s methods.
The server pushes plugins, stores them compressed in the registry under HKCUSoftwareMicrosoftIME, and then loads them in memory. Plugins reach the server through the client as a relay.
The handshake uses the default token “Dmtp”, and packets begin with the magic bytes “dm”.
The Sogou operation followed the QuickFox supply-chain attack. Fortinet reported that a trojanized QuickFox VPN and game-accelerator installer, active since at least August 2025, ran process-based guardrails before deploying FDMTP.
Fortinet’s report noted that an earlier FDMTP campaign used a Sogou Pinyin component, biz_render.exe, for side-loading. Sogou has drawn scrutiny before, including a Citizen Lab analysis of its encryption flaws and Gen Threat Labs’ disclosure of CVE-2026-51990.
ESET reported the weakness on September 11, and Tencent acknowledged it on September 21. Tencent’s version 16.10 moves the affected requests to HTTPS and enables certificate pinning.
ESET’s CNA assigned CVE-2026-120422 on November 2. Users should update Sogou Input Method immediately.
Defenders should hunt for sogou-cdn[.]com, the two staging IPs, a renamed biz_helper.exe in Sogou directories, and unexpected libcef.dll files. They should also secure routers and DNS settings.
IOCs
| IP | Domain | Hosting provider | First seen | Details |
| N/A | blog.wangmengfun[.]top | N/A | 2026‑07‑08 | DarkVigil bootstrap domain. |
| N/A | update.mssproxy[.]net | N/A | 2026‑08‑06 | DarkVigil bootstrap server. |
| N/A | img.fusfun[.]top | N/A | 2026‑08‑06 | DarkVigil bootstrap server. |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.