The cybersecurity agency says it wants to help network defenders prioritize the fixes that matter the most.
The cybersecurity agency says it wants to help network defenders prioritize the fixes that matter the most.
A report by VulnCheck shows nation-state hackers often target flaws in aging routers, firewalls and VPNs. Source link
CrowdStrike Holdings Inc. said Chief Security Officer Shawn Henry will retire from his current role at the company as of March 31, according to a…
An international coalition led by Microsoft and Europol has taken down the operations of Tycoon 2FA, a notorious phishing-as-a-service platform that helped cyber criminals gain…
The vulnerability in a vital defensive technology creates serious risks for federal networks, CISA said. Source link
Federal authorities and security researchers are warning about a critical vulnerability in Fortinet FortiCloud single sign-on, which is currently under exploitation. The flaw, tracked as…
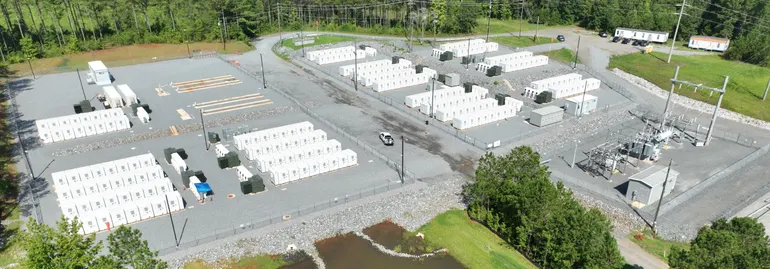
Utility-scale battery energy storage systems are facing heightened risks of attack from nation-state and criminal threat groups, and immediate action needs to be taken to…