Dread, one of the best-known Tor-based discussion forums used by dark web market communities and cybercrime watchers, appears to have been hijacked by unknown operators who claim to control the project’s domain keys.
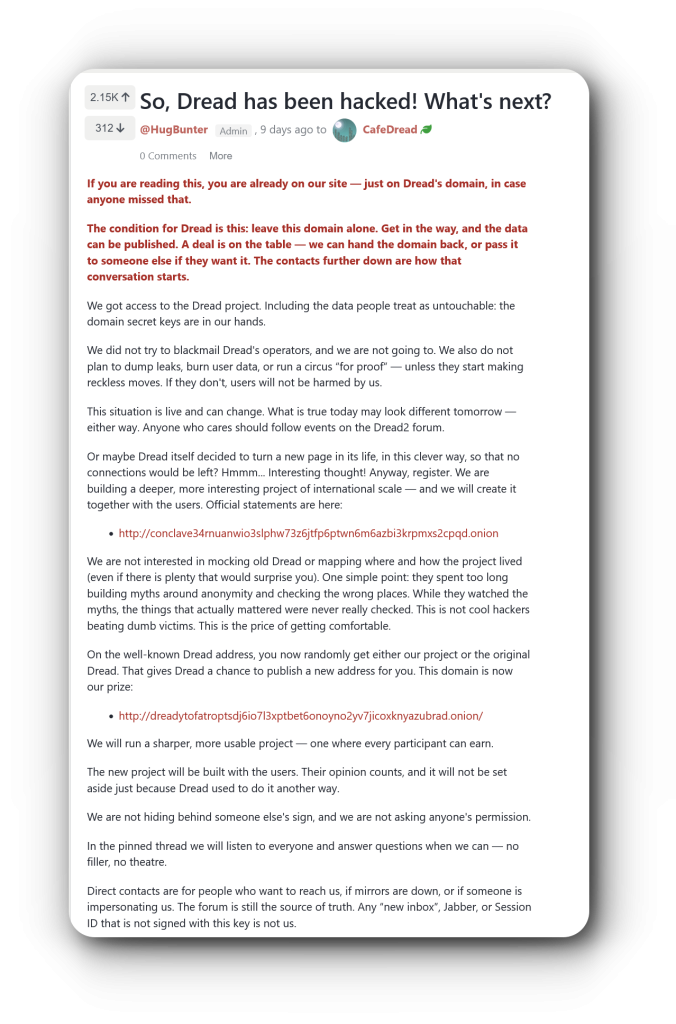
Hackread.com accessed Dread and captured screenshots showing a new pinned post titled “So, Dread has been hacked! What’s next?” The post was published by an account named “HugBunter,” the same handle used by Dread’s long-time administrator, though the authenticity of the account control could not be independently verified.
The screenshots were taken two days before publication. At that time, the pinned hack notice showed it had been posted 9 days earlier, indicating that the claim had remained visible on Dread for more than a week.
A pop-up message shown on the forum states: “Dread has been hacked.” It claims the new operators have the Dread project, including its domain keys, but says they are not blackmailing anyone and are not dumping user data.
New Operators Claim Control of Dread Domain
The pinned post says readers are already on the new operators’ site and that it is being served through Dread’s own domain. The message claims the group has access to the project’s “secret keys” and warns Dread’s operators not to interfere.
The post also says a deal is possible, claiming the domain can be handed back or passed to another party. It does not provide technical proof, but the ability to display messages through the forum’s interface would be a serious sign that the attackers had gained control over part of Dread’s infrastructure or signing setup.
For context, Dread is not a dark web market itself. It functions more like a Tor-based Reddit, with communities discussing darknet markets, scams, arrests, privacy, operational security and cybercrime activity. That makes any takeover significant because many users treat Dread as a source for market status, scam warnings and verified community announcements.
Claim Says User Data Will Not Be Published
The operators behind the post claim they do not plan to publish user data, burn accounts or leak information “unless” Dread’s operators make what they describe as reckless moves.
However, that claim remains unverified and does not show evidence of what data, if any, was accessed. They also do not confirm whether private messages, account records, moderation logs, keys or backend systems were exposed.
The post also includes contact details, a PGP-signed message block and a PGP public key. It tells users that Jabber and Session contacts are temporary, while the PGP fingerprint should be treated as the permanent credential for verifying future messages.
CafeDread Promoted as Replacement Forum
The same post promotes a new forum called CafeDread and encourages users to register. It says shops and users can create their own forums and threads, including hidden VIP areas for selected people.
The message also says Dread’s known address may randomly show either the original forum or the new project, suggesting some kind of domain, mirror or routing conflict. Hackread.com has not independently confirmed the technical cause.
For now, users should visit all Dread-related announcements, mirrors and replacement links with caution. If the claims are accurate, Dread’s operators may have lost control of key infrastructure used to establish trust with users. If the claims are not accurate, the incident may still involve a convincing impersonation or partial compromise.
Until Dread’s original operators verify control through a trusted channel, users should avoid logging in through new mirrors, following replacement links or trusting private messages claiming to represent the forum.
At the time of writing, the Dread forum was offline.