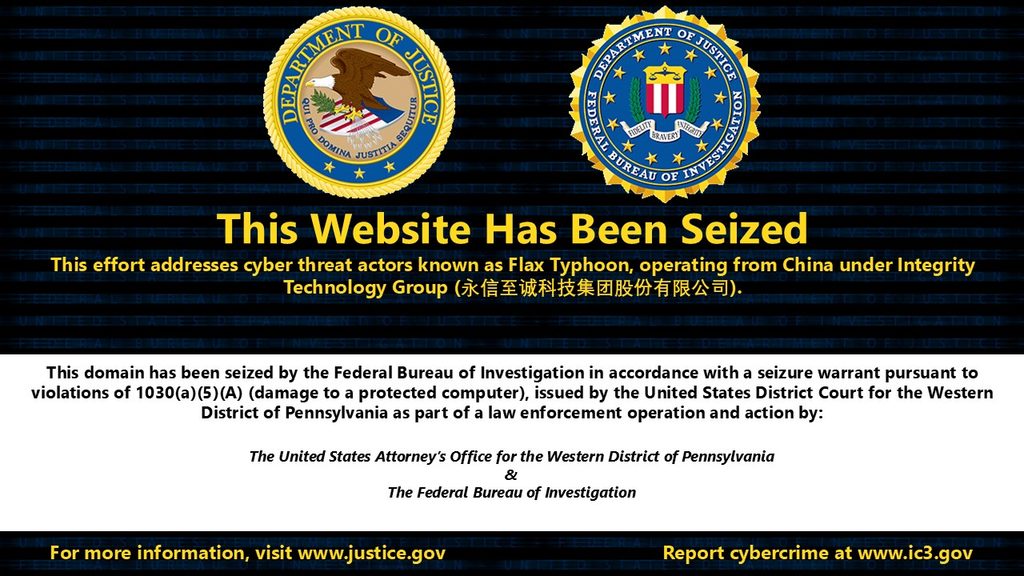
The FBI and DOJ seized domains and disrupted scanning and spear-phishing tools used by Flax Typhoon, a China-linked threat group tied to Integrity Technology Group.
The FBI and US Justice Department have seized 7 domains and disrupted online platforms used by Flax Typhoon, a China-linked hacking group associated with Integrity Technology Group.
According to the Justice Department, the seized infrastructure supported vulnerability scanning and spear-phishing activity used to target US critical infrastructure and foreign networks. The FBI said the platforms were used to scan, and in some cases infiltrate, critical infrastructure systems.
The tools were identified as “Microscan” and “FishHub.” Microscan was used for vulnerability scanning, while FishHub supported spear-phishing operations, according to the Justice Department.
Flax Typhoon has previously been linked to large-scale botnets, living-off-the-land techniques and hands-on exploitation. US authorities associate the group with the now-sanctioned Integrity Technology Group, a China-based company accused of supporting cyber activity for the People’s Republic of China.
In a press release, the Justice Department said the disruption targeted the group’s hacking tools, not just one set of servers. The action is part of a wider US effort to expose companies and contractors accused of helping Chinese state-linked cyber operations.
The Justice Department identified the following domains as part of the seized infrastructure used to support the Flax Typhoon tools:
C0CC.CC98AICAI.COM98AIBLOG.COM98AICODE.COMLINKEDINNS.NETOUTLOOK3650.COMYOUTUBECARD.COM
The FBI, CISA, NSA and international partners also issued a joint cybersecurity advisory (PDF) with technical details, indicators of compromise, tactics, techniques and mitigation guidance for network defenders.
Previous Flax Typhoon Activity
The latest DOJ action follows earlier warnings and enforcement activity involving Flax Typhoon and Integrity Technology Group. In 2023, Microsoft identified Flax Typhoon as a China-linked threat group conducting cyber espionage against government agencies, education, manufacturing, information technology and other sectors.
Microsoft said the group relied heavily on living-off-the-land techniques, using legitimate Windows tools and remote access software to maintain access while reducing the chance of detection.
The group has also been linked to the Raptor Train botnet, a large network of compromised internet-connected devices that US authorities disrupted in 2024. That botnet was associated with Flax Typhoon activity, but “Flax Typhoon” refers to the threat actor, while “Raptor Train” refers to the botnet infrastructure used in the campaign.
Nevertheless, organizations in critical infrastructure sectors should review the advisory, check for listed indicators and look for signs of scanning, spear-phishing and botnet-linked activity associated with the group.