
Hacking on Bug Bounties for a Living

Source link
Related Articles
All Mix →
Your Java builds might break starting January 13th (if you haven’t yet switched repo access to HTTPS) – Alphabot Security
Table of Contents Summary Artifact repositories that will disable HTTP access JCenter (JFrog Bintray) Maven Central Spring (Pivotal) Gradle Conclusion Summary This blog post is…
UL NO. 442: Crowdstrike Analysis, Cannabis=Soma?, NK Github SE, AI Weaponry
Table of Contents TOC NOTES MY WORK SECURITY AI / TECH HUMANS IDEAS DISCOVERY RECOMMENDATION OF THE WEEK APHORISM OF THE WEEK SECURITY | AI…
How to Use Hugging Face Models with Ollama
Ollama is one of my favorite ways to experiment with local AI models. It’s a CLI that also runs an API server for whatever it’s…
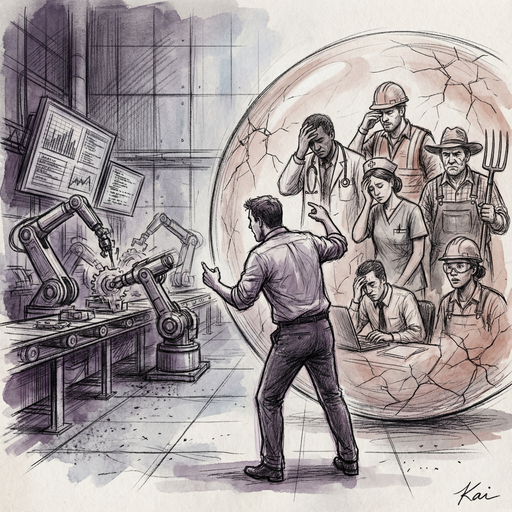
The Bubble Is Labor | Daniel Miessler
I can’t remember when I realized this, but I want to say it was less than five or ten years ago. Scared the crap out…
community/KCSA-CVE-2020-28914.md at main · kata-containers/community · GitHub
announcement-date: 2020-11-17 id: KCSA-CVE-2020-28914 title: Kata Containers Improper file permissions for read-only volumes description: An improper file permissions vulnerability affects Kata Containers prior to 1.11.5.…
Why aren’t you able to do BUG BOUNTIES or Anything?
Why aren’t you able to do BUG BOUNTIES or Anything? Source link