
How to Hunt for Prototype Pollution Vulnerabilities in Open Source Bug Bounty | #methodology

Source link
Related Articles
All Mix →
A security overview of Content Management Systems
Table of Contents Deciding between closed- vs open-source CMS platforms: How to secure your CMS or blog site: Expert point of view: how secure are…

Burp Suite Enterprise Edition Kubernetes deployment and auto-scaling | Blog
Table of Contents Scan your web portfolio more economically Fast, seamless integration with your Kubernetes infrastructure Migrating from a legacy cloud template deployment We're here…
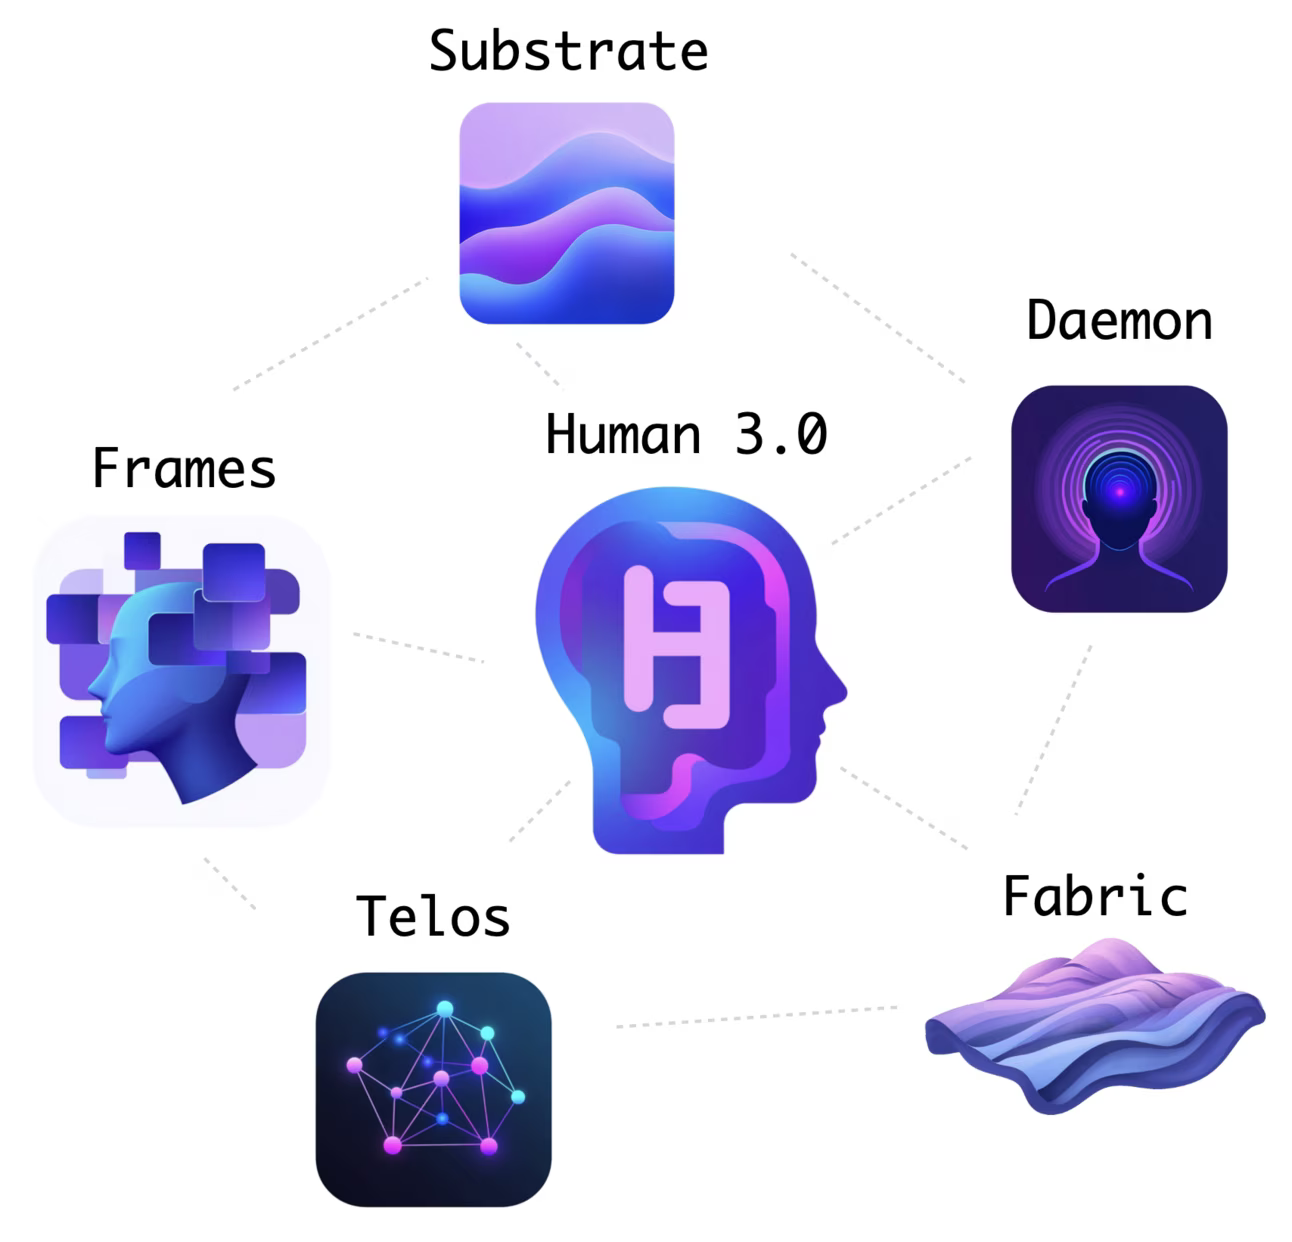
How My Projects Fit Together
Table of Contents The Problem(s) Security forever The projects Substrate Fabric TELOS Daemon Human 3.0 How they all fit together Summary When people look at…
Hacker-Powered pen tests at the U.S. Federal Government
When looking for a model to inform your own security posture, the Department of Defense would be a good place to look. Not only were…
My Thoughts on Depression | Daniel Miessler
A new BBC piece is highlighting an alternate approach to depression. Rather than assume that it’s something that should immediately be countered with drugs, how…
Learn to Hack Web Apps – Live | #APIs #BOLA #brokenAuth
Learn to Hack Web Apps – Live | #APIs #BOLA #brokenAuth Source link