$536 and 8 Hours: AI Learns to Attack a Different PLC
$536 and 8 Hours: AI Learns to Attack a Different PLC Pierluigi Paganini September 02, 2026 Experts got Claude to port a PLC exploit, but…
$536 and 8 Hours: AI Learns to Attack a Different PLC Pierluigi Paganini September 02, 2026 Experts got Claude to port a PLC exploit, but…
The Federal Communications Commission wants to set up a new scorecard system that would allow consumers to rate their telecoms’ ability to prevent or deter…
The average adversary breakout time is now 29 minutes, with the fastest recorded at 27 seconds, according to the CrowdStrike 2026 Global Threat Report. AI is…
The vulnerability was assigned a critical severity (CVSS 9.8) and affects several self-hosted Artifactory release branches. JFrog has released fixes for affected self-hosted versions, while…
Today, we are proud to announce that Wiz for Government has achieved FedRAMP® Moderate authorization just four years since the company was founded. This achievement,…
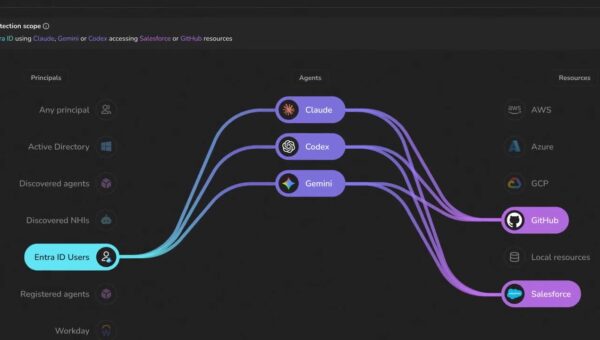
AI agents are evolving identity as we know it. They execute code, invoke tools, access applications and sensitive data, and take action on behalf of…
When we launched the Huntress API in 2022, the goal was straightforward: give partners a way to pull their Huntress data without logging into the…
A critical authentication bypass vulnerability (CVE-2026-82329) in JFrog Artifactory is being exploited in attacks to create tokens that provide administrative access. The flaw is present…
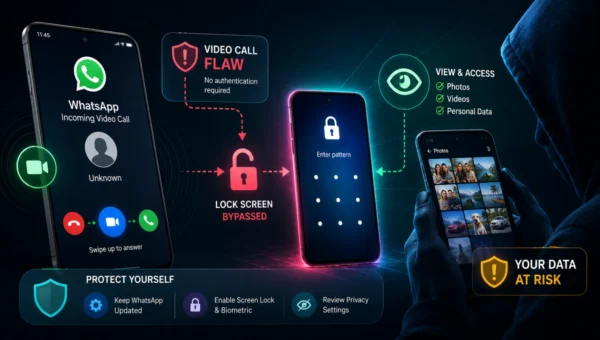
A newly disclosed WhatsApp flaw on Android is raising fresh privacy alarms, allowing anyone holding a locked phone to browse through its entire photo gallery…
KnowBe4 has appointed cybersecurity channel veteran Kurt Mills as its new channel chief, as the company looks to strengthen its global partner ecosystem and expand…
Security teams rarely struggle because they lack data. More often, the challenge is deciding which signals actually deserve attention. Modern security environments generate information about…
Nearly 22,000 Microsoft Exchange servers remain unpatched against CVE-2026-62911, a critical authentication bypass vulnerability, according to daily scans from the Shadowserver Foundation. The United States…