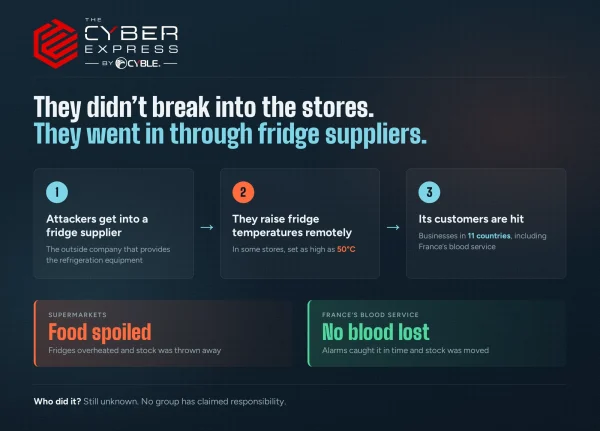
Until this week, the wave of refrigeration cyberattacks sweeping Europe looked like a supermarket problem. That changed when France’s national blood service confirmed that temperature controls had been altered at three of its sites. Blood products stored for hospitals were suddenly at risk, and the attackers had not even targeted the organisation directly.
The Établissement Français du Sang (EFS) said “temperature and defrosting thresholds were raised to very high levels” in its cold storage rooms. These rooms hold blood products at preparation and distribution sites before they go to healthcare facilities, along with samples for biobanks.
The outcome was far better than in the supermarkets. “No health impacts have been identified and no losses of blood products have been reported,” the EFS said in a statement on Tuesday.
How the Refrigeration Cyberattacks Reached Blood Storage
The EFS says it was not targeted directly. Like many of the affected retailers, it says the attack reached it through a third-party provider of refrigeration equipment.
That detail explains why a blood service ended up on the same list as supermarkets. If attackers can get into a shared supplier’s systems, any organisation using that equipment may be exposed, whatever its sector.
This is the first reported case in France in the second wave of attacks on control systems, and the first reported to affect a healthcare organisation.
Why the Blood Supply Survived When Food Did Not
The difference came down to how quickly someone noticed. “The EFS’s monitoring and alarm systems enabled the rapid identification of these anomalies and the implementation of necessary measures to ensure that no blood samples or products were compromised,” the organisation said.
Depending on the situation, affected equipment was either brought under control without impacting the products, or shut down. Products in the affected cold rooms were moved to other facilities as a precaution.
Compare that with the first wave in France in October. Attackers remotely defrosted fridges in hundreds of supermarkets, reportedly by triggering a forced defrost option, and pushed temperatures as high as 50 degrees Celsius. They struck while stores were closed, so the heat went unnoticed for hours. Tonnes of food perished, some equipment melted, and in some stores the heat sparked fires. Reporting on that wave found the attackers had targeted ageing, internet-connected devices still online years after their manufacturer stopped supporting them.
How Far the Refrigeration Cyberattacks Have Spread
The second wave is wider than the first. Businesses in at least 11 countries have reportedly been affected: Belgium, Estonia, Finland, France, Germany, Ireland, Luxembourg, the Netherlands, Portugal, Sweden and the United Kingdom.
Earlier this week, supermarket chains in Sweden, Belgium, Luxembourg, Ireland and Estonia reported fridges and freezers set to high temperatures, with several discarding food. In Estonia, where the intrusion was caught within minutes, there was no significant damage.
Who Is Behind It?
No one knows for sure, and no group or entity has claimed responsibility for the attacks. It is also unclear whether the same people are behind both waves.
Rumours have spread online that two Russian hacktivists groups, Noname057(16) and Z-Pentest Alliance, posted that they had hacked Danfoss. That led to speculation that they were behind the freezer attacks. Analysts now question whether that claim means they were responsible.
Russian groups have not been ruled out. However, experts say Iranian hacktivists, nation-state hackers, or even teenagers pulling pranks could also be the culprits.
A French Bank Reports a Separate Attack
In the same week, Crédit Mutuel Arkéa in northwestern France said it had halted some services after a cyberattack enabled fraudulent transactions. Nothing in the bank’s statements links the incident to the refrigeration attacks. However, the bank describes a similar entry point: attackers “used the platform of one of our service providers” to reach the bank directly.
The bank said attackers used its own account, not customer accounts, to make transactions to other banks. That potentially let them convert the money into cryptocurrency through specialised platforms. It denied press reports that the attackers got in through its subsidiary Fortuneo, and said human error was not the cause.
Asked whether 118 million euros was stolen, the bank said it could not confirm the figure and could “only validate the order of magnitude.” Some funds have been frozen and recovery efforts are under way. The bank says the losses will not threaten its financial stability and that customers’ assets were not affected, apart from delays to some transfers. Almost all operations have resumed.
The bank has also warned customers about a likely rise in phishing attempts, urging them never to share passwords, card numbers or SMS validation codes.
The refrigeration attacks and the bank attack have not been tied to the same attackers. What they share is the route in. In both cases, the organisations say they were reached through an outside provider rather than through their own systems. Neither the blood service nor the bank was the first door the attackers opened.