WordPress To Mandate 2FA for Theme And Plugin Developers
Beginning on October 1st, 2024, WordPress will mandate two-factor authentication (2FA) for plugin and theme creators as a new security measure. Themes and plugins that…
Beginning on October 1st, 2024, WordPress will mandate two-factor authentication (2FA) for plugin and theme creators as a new security measure. Themes and plugins that…
Banking malware is a type of malicious software that targets financial institutions and their customers. There is a rise in Android banking malware, which exploits…
Once upon a time, I.T. security teams depended on hodgepodges of different cybersecurity solutions from various vendors. However, these multivendor tech stacks became prohibitively costly…
Lazarus Group is a notorious APT hacker group believed to be state-sponsored by North Korea, primarily linked to the country’s intelligence agency. This group has…
Threat actors often exploit legitimate software for malicious purposes as it enables them to evade security measures and gain unauthorized access to systems. By using…
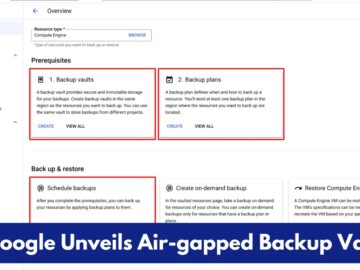
Google Cloud has introduced air-gapped backup vaults as part of its enhanced Backup and Disaster Recovery (DR) service. This new feature, currently available in preview,…
GitLab has released a critical security update addressing several vulnerabilities; among them critical ones are CVE-2024-6678, CVE-2024-8640, CVE-2024-8635, and CVE-2024-8124. GitLab recommends that all installations…
The Kali Linux team has released Kali Linux 2024.3, the latest iteration of their popular penetration testing and ethical hacking distribution. This update brings a…
Security researchers have discovered a critical vulnerability in the domain validation process that could potentially compromise the security of the entire .mobi top-level domain (TLD).…
Cynet upended the security vendor market with an All-in-One Cybersecurity Platform that combines a full suite of must-have capabilities on a single, simple solution, backed…
Cybersecurity researchers at Unit 42, a division of Palo Alto Networks, have uncovered a new and sophisticated phishing technique that exploits the refresh entry in…
Hackers target SMBs (Small and mid-sized businesses) primarily as they are often easier to compromise with due to weaker security measures and a lack of…