Iranian Cyber Actors Deploy Malware Via Telegram, FBI Warns
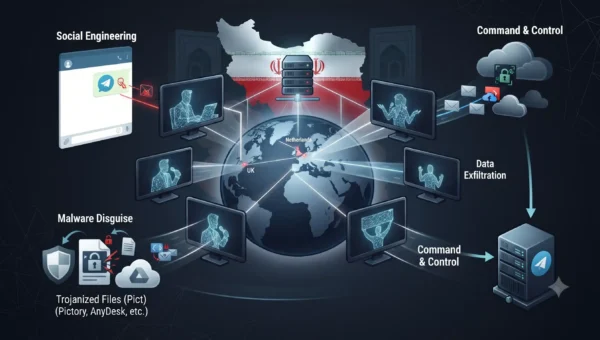
Iranian cyber actors are using a malware family known as HEAVYGRAM, also tracked as CHOSEN BRICK, to target dissidents, journalists, and opposition groups worldwide, according…
Iranian cyber actors are using a malware family known as HEAVYGRAM, also tracked as CHOSEN BRICK, to target dissidents, journalists, and opposition groups worldwide, according…
The Thinkng Bull cyberattack targeted the Seoul-based math academy headquartered in Daechi-dong. The attack has exposed the personal information of students and parents, drawing scrutiny from…
Microsoft released patches for 18 vulnerabilities on Thursday, spanning its Azure cloud portfolio and Copilot-branded AI products. Elevation of privilege flaws made up the bulk…
U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog Pierluigi Paganini September 17, 2026 U.S. Cybersecurity and Infrastructure Security…
North Korean hackers are infiltrating tens of thousands of job seekers’ computer networks by posing as prospective employers, such as artificial intelligence firms, to steal…
In Silicon Valley and beyond, the architects of artificial intelligence are increasingly warning about the risks it poses to humanity. Anthropic CEO Dario Amodei wants…
Microsoft 365 users are being tricked into handing over access to their accounts by a new phishing kit, GhostCode, that exploits a weakness in a…
A 2021 report from Google’s Cybersecurity Action Team mentioned that in 50 compromised Google Cloud instances they had investigated, 86% were used for cryptocurrency mining.…
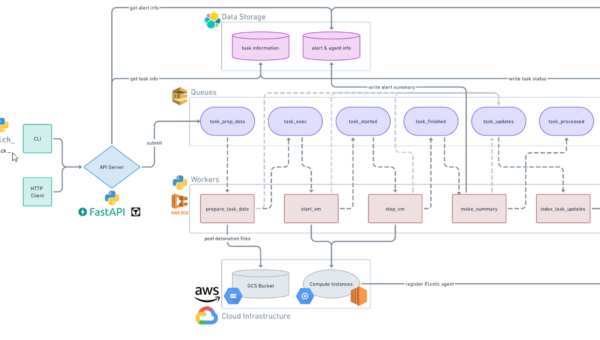
Preamble In our first post in our Detonate series, we introduced the Detonate system and what we use it for at Elastic. We also discussed…
Collaboration suites like M365 offer unparalleled convenience. Millions of teams rely on them to quickly share documents with coworkers, clients and business partners. Yet when…
Today is World Quantum Readiness Day, and this year’s theme, “From Blueprint to Build,” says a lot about where the industry has landed. Three years…
A newly observed ransomware operation dubbed SETTRA is abusing the legitimate MeshAgent remote monitoring and management platform for persistence while using recovery-inhibition and defense-evasion techniques…