Early Scattered Spider member pleads guilty to cybercrime spree
Another core member of the hacker subset of The Com involved in a spree of extortion attacks from at least 2021 to 2023 pleaded guilty…
Another core member of the hacker subset of The Com involved in a spree of extortion attacks from at least 2021 to 2023 pleaded guilty…
The rise in AI-generated security threats may just have generated one casualty: the death of the weekly bulletin of security threats from the US Cybersecurity…
SANS Institute published Dynamic Incident Response: A Framework for Security Teams by SANS Fellow Joshua Wright, the first major rebuild of the SANS incident response…
In the business of cloud computing, achieving a state of perfect security is almost like scaling a digital mountain summit. It requires not only technical…
Key takeaways li]:list-disc”> How Elastic Security Labs identified reconnaissance from the adversary group The adversary’s steps to evade detection using xcc , installing the sh.py…
The Gyazo image-sharing platform has confirmed it suffered a data breach after hackers exploited a server vulnerability that allowed them to steal 23.6 million user records.…
Feral Wolf is using exposed business software and weak server settings to reach corporate networks, then locking files with ransomware. The campaign shows how one…
40% of organisations have suffered an AI-related compliance or governance issue in the last 12 months, with legacy and poorly designed business processes identified as…
Before two of its alleged members were arrested and charged in Australia last month, the hacker group known as TeamPCP carried out a hacking spree…
Feral Wolf has expanded its ransomware tradecraft by abusing exposed Atlassian Confluence servers and insecure 1C:Enterprise deployments to gain access to Russian corporate networks before…
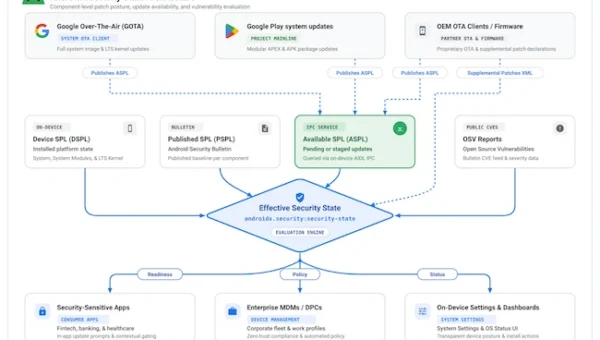
New AndroidX Security State libraries provide a more granular way to determine how securely patched an Android device is. The stable Security State v1.1.0 and…
Researchers at Zimperium’s zLabs have analyzed an Android Trojan that uses an automated, multi-stage infection process. What’s new is that RatHat gives a live AI…