

Related Articles
All Mix →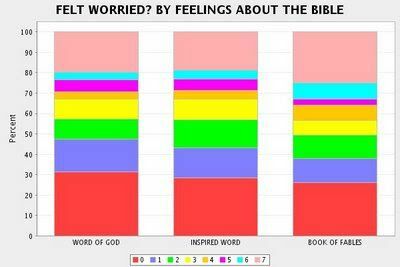
Believers Worry Less Than Non-Believers
This is an interesting piece over at the Audacious Epigone. It shows that the deeply religious worry the least, which makes perfect sense to me.…
Free Will Revisited | Daniel Miessler
Table of Contents Basics What Now? Maximizing Happiness Best Case as No Possibility of Suffering? Summary At a recent team meetup in Atlanta I had…
What Juneteenth Means at HackerOne
This year, the Juneteenth holiday gained wider global recognition. At HackerOne, we kicked off our inaugural Juneteenth celebration with a day of learning, reflection and unified…
A complete guide to exploiting advanced SSRF vulnerabilities
SSRF—short for Server-Side Request Forgery—vulnerabilities are amongst one of the most impactful web security vulnerabilities. Even though they are less commonly found on targets they…

The surprisingly difficult task of printing newlines in a terminal
Your guide to string interpolation quirks that confound the best of us. Surprisingly, getting computers to give humans readable output is no easy feat. With the…
Why Prompt Engineering and Context Engineering Both Miss the Point
Table of Contents The Director Analogy The Prompting Answer The Context Engineering Answer The Real Skill Summary There’s a popular idea going around right now…
Impact
When using
--userns-remap, if the root user in the remapped namespace has access to the host filesystem they can modify files under/var/lib/docker/that cause writing files with extended privileges.Patches
Versions 20.10.3 and 19.03.15 contain patches that prevent privilege escalation from remapped user.
Credits
Maintainers would like to thank Alex Chapman for discovering the vulnerability; @awprice, @nathanburrell, @raulgomis, @chris-walz, @erin-jensby, @BassMatt, @mark-adams, @dbaxa for working on it and Zac Ellis for responsibly disclosing it to security@docker.com