Ukrainian Hive and Nefilim Ransomware Affiliate Gets 70 Months in US Prison
A 36-year-old Ukrainian national was sentenced to prison in the US for his role in Nefilim ransomware attacks. The man, Artem Aleksandrovych Stryzhak, who had…
A 36-year-old Ukrainian national was sentenced to prison in the US for his role in Nefilim ransomware attacks. The man, Artem Aleksandrovych Stryzhak, who had…
Ads or Surveillance? Researchers Flag Suspicious Targeting of Starlink Users Pierluigi Paganini October 28, 2026 Discover-Tech allegedly targeted Starlink users with digital ads to track…
Lucy Ashall | Wednesday, 28 October 2026 at 15:32 UTC Join us at booth G14 on 5–6 November at the Hyatt Regency San Francisco. We’re…
A systemic cyber event could lead to billions of dollars in claims that exceed current risk models. Source link
Volt Typhoon, a China-government backed hacking group that has infiltrated America’s critical infrastructure networks for years, has consistently built and dismantled ephemeral malicious infrastructure to…
A threat actor dubbed Gheist is turning compromised GitHub accounts into credential-harvesting platforms. By planting malicious GitHub Actions workflows in private repositories, the attackers can…
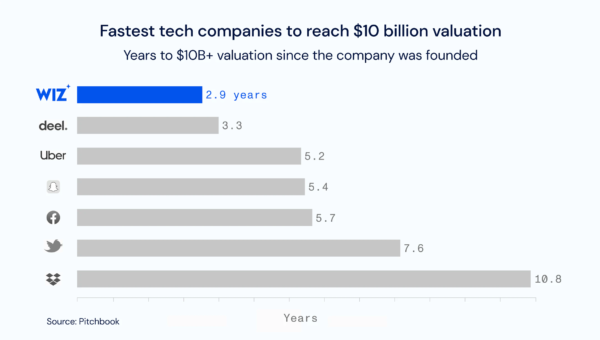
When we started Wiz just over three years ago, we set out to help security and dev teams transform their security operation model to the…
Ransomware gang begins leaking data on GMO customers. Business news: Blackwall (formerly BotGuard) raises $100 million. Source link
Chinese state-sponsored hacking group Volt Typhoon has been using a framework that relies on rotating chains of connected devices compromised on demand, including for zero-day…
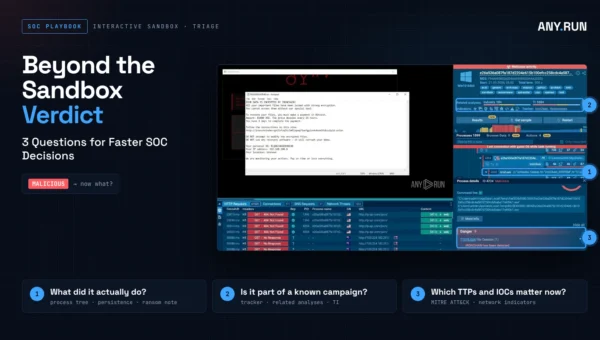
Whether you’re investigating a suspicious URL or a file, you need more than a verdict to make a confident, evidence-based decision. You need to understand…
Application security vendor Black Duck has launched Signal Agentic Fix, a new AI agent designed to shrink the gap between vulnerability discovery and a validated…
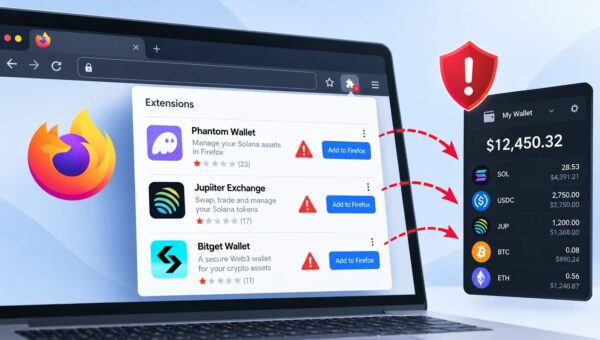
Three malicious Firefox extensions impersonating Phantom, Jupiter, and Bitget to steal cryptocurrency wallet recovery phrases and private keys. The campaign combines deceptive branding, bundled credential…